Notespaceos
spaceos 时间:2021-03-28 阅读:()
One-byteModificationforBreakingMemoryForensicAnalysisTakahiroHaruyama/HiroshiSuzukiInternetInitiativeJapanInc.
forsubmissionMemoryForensicsOverview–MemoryAcquisition–MemoryAnalysisPreviousWorks:AntiMemoryForensicsProposedAntiAnalysisMethodImprovementPlansWrap-upSummary2MEMORYFORENSICSOVERVIEW3Analyzingvolatiledataisimportanttodetectthreatsquickly–increasingamountsofdiskdata–antidiskforensicmethodsusedbymalwaresMemoryforensicsbecamepopularoverthelastfewyears2stepsformemoryforensics–memoryacquisitionandmemoryanalysis4What'sMemoryForensicsTargetMachineInvestigator'sMachineMemoryImageFile1.
AcquireRAMdataasanimagefile2.
ParseandanalyzetheimageofflineOfflineparsingamemoryimagedoesn'tusesystemAPIsMemoryforensicscanget–unallocateddata(e.
g.
,terminatedprocess)–datahiddenbymalware(e.
g.
,hiddenprocess)5WhyMemoryForensicsLiveResponseToolMemoryForensicAnalysisToolRunningProcessHiddenProcessTerminatedProcessAllocatedUnallocatedWindowsAPIParsebinaryimageandextractinformationfromitGetinformationthroughsystemAPIRawImageAcquisition–HBGaryFastDumpPro[1]–GuidanceWinEn[2]–MoonSolsWindd[3]CrashDumpImageAcquisition–MoonSolsWinddMemoryImageConversion–MoonSolsWindowsMemoryToolkit[3]6SomeFormats/AcquisitonToolsMemoryImageFileCPURegisterIncludedCrashDumpHibernationNotIncludedRawDifferencebetweenRawImageandCrashDumpCrashdumpfiledoesn'tinclude–1stPage–PagesreservedbydevicesRun[0]BasePage=0x1,PageCount=0x9eRun[1]BasePage=0x100,PageCount=0xeffRun[2]BasePage=0x1000,PageCount=0xeef0Run[3]BasePage=0xff00,PageCount=0x1001stPage(BIOSReserved)AddressSpaceReservedbyDevices(NotIncludedincrashdump)PhysicalMemoryAddressSpace(e.
g.
,256MBRAM)7EvaluationofMemoryAcquisitionToolsCanrawimageacquisitiontoolsget1stpageanddevice-reservedpages[4]–WinEn–Win32dd/c0MemoryContent(/c)option–Caution:/c0optionmaycauseBSODonx64machineWinEnFDProWin32dd/c0Win32dd/c1Win32dd/c21stPageDevicereservedpages8AnalysisExample:MakingObjectCreationTimeline9VolatilityFramework[5]–timelinerplugin[6]usedkernelobjects(process/thread/socket)eventlogsSpyEyebot(deadprocess)TCPconnectionestablishedbyexplorer.
exeCodeinjectionactivityAnalysisExample:DetectingCodeInjection10Detectingcodeinjection–VolatilityFrameworkmalfind–EnCaseEnScript[7]VadDump–MandiantRedline[8](GUIfront-endforMemoryze[9])ThetoolscheckprotectionflagofVirtualAddressDescriptorMandiantRedline(Memoryze)HBGaryResponderVolatilityFramework2.
0EnCaseEnScirptSupportedWindowsOSAllAllXP/Vista/7/2003/2008XP/7/2003/2008SupportedImageFormatRawRawRawCrashdumpHibernationRawCrashdumpSupportedCPUArchitectureIntelx86AMDx64Intelx86AMDx64Intelx86Intelx86AMDx64Extractingdeadprocess/closedconnectionNoNoYesYesNoteMalwareRiskIndex,MemD5DigitalDNA,codegraphingOpensource,richpluginsMultilingualsearch,EntropyComparisonofMemoryAnalysisTools11PREVIOUSWORKS:ANTIMEMORYFORENSICS12ShadowWalkerisproposedbySherriSparksandJamieButlertohidemaliciousmemoryregions–Installedpagefaulthandlermakesde-synchronizedDTLB/ITLBdataaccess->randomgarbagedataexecuteaccess->rootkitcodeMemoryacquisitiontoolscannotpreventShadowWalkerfromhidingmemorypages–ButAnalysistoolscandetecttheIDThooking13AntiAcquisitionMethods:ShadowWalker[10]Proofofconceptscript–killingspecifiedprocessesorpreventingdriverloadingswiththeaimofmemoryacquisitionfailureVeryeasytoimplement–Theevasionisalsoeasy(e.
g.
,randomname)–Preventingdriverloadingshasanimpactontherunningsystem14AntiAcquisitionMethods:MeterpreterAntiMemoryForensicsScript[11]Objectcarvingisonetechniquetoextractkernelobjectinformation–e.
g.
,processobject(_EPROCESS)PTFinder:Type/Sizein_DISPATCHER_HEADERVolatilityFramework:PoolTagin_POOL_HEADERBrendanDolan-Gavittetal.
warnedanattackercouldchangethevaluestohideaspecifiedobject[12]–Instead,theyproposedrobustsignaturescausingBSODorfunctionalityfailuresifthevaluesarechanged15AntiAnalysisMethod:AntiObjectCarvingmodifyingheadervaluesofcmd.
exeClosed-sourceanalysistoolscanfindthehiddenprocess–HowdotheyfinditOtherthanobjectcarving,thereareseveralkeyoperationsforanalyzingmemoryimage–TheoperationsarerobustLet'scheckit!
16AntiAnalysisMethod:AntiObjectCarving(Cont.
)MemoryzeHBGaryResponderPROPOSEDANTIANALYSISMETHOD17Researchedimplementationsofthreemajortools–VolatilityFramework2.
0–MandiantMemoryze2.
0–HBGaryResponderCommunityEdition2.
0Foundthreeoperationsexecutedinmemoryanalysisincludeafewunconsideredassumptions–Proposedmethodmodifiesone-byteofdatarelatedtotheoperationsThedataisdefinedas"AbortFactor"–Itcan'thidespecificobjects,butcanabortanalyses–NoimpactontherunningsystemNoBSOD,noerrorsforafewdaysto2weeks18AbstractofProposedMethodVirtualaddresstranslationinkernelspaceGuessingOSversionandArchitectureGettingkernelobjects–traversinglinkedlistsorbinarytrees–objectcarving19SensitiveThreeOperationsinMemoryAnalysisVirtualaddresstranslationinkernelspaceGuessingOSversionandArchitectureGettingkernelobjects–traversinglinkedlistsorbinarytrees–objectcarving20SensitiveThreeOperationsinMemoryAnalysisOSswitchesitscontextbyloadingDirectoryTableBase(DTB)ofeachprocess–DTBisstoredineachprocessobject(_EPROCESS)Initially,analysistoolsmustgetDTBvalueforkernelspaceTwoprocesseshavethekernelDTB–PsInitialSystemProcess(Systemprocess)–PsIdleProcess(Idleprocess)21VirtualAddressTranslationinKernelSpaceOSloadsDirectoryTableBase(Startphysicaladdressforaddresstranslation)intoControlRegister(CR3)x86AddressTranslation-HowPAEX86Workshttp://technet.
microsoft.
com/en-us/library/cc736309(WS.
10).
aspx22VirtualAddressTranslationinKernelSpace:ProcessObjectStructure_POOL_HEADER_OBJECT_HEADER_EPROCESS_KPROCESS_DISPATCHER_HEADERPoolTag:"Pro"TypeandSizeDTBImageFileName:"System"or"Idle"FlagsSearch_DISPATCHER_HEADERtoget_EPROCESSCheckwhethertheImageFileNameis"Idle"–IftheprocessisIdle,getDTBvaluein_KPROCESS23VirtualAddressTranslationinKernelSpace:VolatilityFramework_DISPATCHER_HEADER(e.
g.
,"x03x00x1bx00")ImageFileNameSearch"System"tofindImageFileNamein_EPROCESSofPsInitialSystemProcessValidatebyusing_DISPATCHER_HEADERinthe_KPROCESS–All_DISPATCHER_HEADERpatternsarechecked24VirtualAddressTranslationinKernelSpace:MandiantMemoryzeOSversion_DISPATCHER_HEADERByteSequenceXP32bit03001B00200332bit03001E00200364bit03002E00Vista32bit03002000Vista64bit03003000732bit03002600764bit03005800Validatebyusingthefollowingvalues–Flagsin_OBJECT_HEADERThedistancebetweenPoolTagand_EPROCESSiscalculatedaccordingtothevalue–PoolTagin_POOL_HEADERSearchPoolTagfrom_EPROCESSpositionandcheckwhetherthesearchhitoffsetisequaltothecalculateddistanceIfalldataisvalid,gettheDTBvalue25VirtualAddressTranslationinKernelSpace:MandiantMemoryze(Cont.
)Search_DISPATCHER_HEADERstoget_EPROCESSGetDTBvaluefromtheresultandvalidateitResponderseemstobeequippedwiththealgorithmguessingkernelDTB–IfDTBsofPsInitialSystemProcessandPsIdleProcessarenotfound,aguessedDTBvalueisused26VirtualAddressTranslationinKernelSpace:HBGaryResponder27VirtualAddressTranslationinKernelSpace:RelatedDataToolRelatedDataAbortFactorRemarksVolatilityFramework_DISPATCHER_HEADERXPsIdleProcessImageFileNamein_EPROCESSXMandiantMemoryze_DISPATCHER_HEADERXPsInitialSystemProcessPoolTagin_POOL_HEADERXFlagsin_OBJECT_HEADERXImageFileNamein_EPROCESSXHBGaryResponder_DISPATCHER_HEADERoriginalguessingalgorithmVirtualaddresstranslationinkernelspaceGuessingOSversionandArchitectureGettingKernelObjects–traversinglinkedlistsorbinarytrees–objectcarving28SensitiveThreeOperationsinMemoryAnalysisSizeanddefinitionofkerneldatastructuresdifferaccordingto–OSversion(e.
g.
,XPSP2/SP3,7SP0/SP1)–architecture(x86andx64)Allanalysistoolsguesstheversionusingdebugstructures29GuessingOSversionandArchitectureOSversion_EPROCESSsize(bytes)WindowsXPSP332bit0x260Windows7SP032bit0x2C0Windows7SP064bit0x4D0WindowsVistaSP232bit0x270WindowsVistaSP264bit0x3E830GuessingOSversionandArchitecture:DebugStructuresandKeyValues_KPCR_DBGKD_GET_VERSION64_KDDEBUGGER_DATA64KdVersionBlockDebuggerDataListHeaderCmNtCSDVersion_DBGKD_DEBUG_DATA_HEADER64OwnerTag:"KDBG"SizeKernBaseKernBasePrcbDataPsActiveProcessHeadPsLoadedModuleList_KPRCBCurrentThreadUsersmustspecifyOSversionandArchitecture–e.
g.
,--profile=WinXPSP2x86Iftheversionisunknown,imageinfocommandcanguessit–scan_DBGKD_DEBUG_DATA_HEADER64[13]31GuessingOSversionandArchitecture:VolatilityFrameworkOwnerTag:"KDBG"SizeSupposedlydetermineOSandarchitecturebasedon_DISPATCHER_HEADERValidatethembyusinganoffsetvalueofImageFileNamein_EPROCESS32GuessingOSversionandArchitecture:MandiantMemoryzeOSversionoffsetvalueofImageFileNameXP32bit0x174200332bitSP00x154200332bitSP1/SP20x164XP/200364bit0x268Vista32bit0x14CVista64bit0x238732bit0x16C7/200864bit0x2E0TrytotranslateavirtualaddressofThreadListHeadin_KPROCESS–Ifpossible,theOSversionandarchitecturearecorrectGetSPversionfromCmNtCSDVersionin_KDDEBUGGER_DATA6433GuessingOSversionandArchitecture:MandiantMemoryze(Cont.
)GetKernBasevalue–_DBGKD_GET_VERSION64or_KDDEBUGGER_DATA64ValidatethePEheadersignatures–DOSheader"MZ"andNTheader"PE"GetOSversion–OperatingSystemVersionsinOptionalHeadere.
g.
,Windows7–MajorOperatingSystemVersion=6–MinorOperatingSystemVersion=1Getmorespecificversion–TimeDataStampinFileheader34GuessingOSversionandArchitecture:HBGaryResponder35GuessingOSversionandArchitecture:RelatedDataToolRelatedDataAbortFactorRemarksVolatilityFramework_DBGKD_DEBUG_DATA_HEADER64XMandiantMemoryze_DISPATCHER_HEADERXPsInitialSystemProcessoffsetvalueofImageFileNameXThreadListHeadin_KPROCESSCmNtCSDVersionin_KDDEBUGGER_DATA64HBGaryResponderKernBasein_DBGKD_GET_VERSION64or_KDDEBUGGER_DATA64PEHeaderofWindowskernelPEheadersignatures"MZ"/"PE"OperatingSystemVersioninOptionalHeaderXTimeDataStampinFileHeaderVirtualaddresstranslationinkernelspaceGuessingOSversionandArchitectureGettingKernelObjects–traversinglinkedlistsorbinarytrees–objectcarving36SensitiveThreeOperationsinMemoryAnalysisTraversinglinkedlistsorbinarytrees–Generally,usespeciallead/rootaddressesPsActiveProcessHeadforprocesslistPsLoadedModuleListforkernelmodulelistVadRootforVirtualAddressDescriptortreeObjectcarving–Generally,usefixedvaluesinheaders_POOL_HEADER_DISPATCHER_HEADERMyresearchfocusedongetting_EPROCESS37GettingKernelObjectsProcesslististwo-waylink–Each_EPROCESSincludesActiveProcessLinks_LIST_ENTRY(FlinkandBlink)–PsActiveProcessHeadandPsInitialSystemProcessarebounduptogether38GettingKernelObjects:ProcessLinkedListPsActiveProcessHead_EPROCESS"System"_EPROCESS"smss.
exe"_EPROCESS"win32dd.
exe"FLINKBLINKFLINKBLINKFLINKBLINKFLINKBLINK.
.
.
.
.
.
.
.
.
Traversinglinkedlistsorbinarytrees–Search_DBGKD_DEBUG_DATA_HEADER64–getPsActiveProcessHeadin_KDDEBUGGER_DATA64Objectcarving–usePoolTagin_POOL_HEADER39GettingKernelObjects:VolatilityFrameworkExecutingKDBGScannerGetting_DBGKD_DEBUG_DATA_HEADER64(=_KDDEBUGGER_DATA64)addressObjectcarving–find_EPROCESSusingaddressvaluese.
g.
,–DTBis0x20-bytesaligned–(Peb&0x7ffd0000)==0x7ffd0000–(ActiveProcessLinks.
Flink&0x80000000)==0x80000000–similartorobustsignaturesproposedbyBrendanDolan-Gavittetal.
[12]40GettingKernelObjects:MandiantMemoryzeTraversinglinkedlistsorbinarytrees–getCurrentThreadin_KPRCB–get_EPROCESSfromthethreade.
g.
,ApcState.
Processin_KTHREAD(XP)–starttotraverseprocesslistfromthe_EPROCESS"System"stringiscomparedwithImageFileNameof_EPROCESS–foridentifyingPsActiveProcessHead–fordetectinghiddenprocess41GettingKernelObjects:HBGaryResponder42GettingKernelObjects:RelatedDataToolRelatedDataAbortFactorRemarksVolatilityFramework_DBGKD_DEBUG_DATA_HEADER64XPsActiveProcessHeadin_KDDEBUGGER_DATA64XPoolTagin_POOL_HEADERMandiantMemoryzeaddressvaluesin_EPROCESS(DTB,Peb,etc.
)HBGaryResponderCurrentThreadin_KPRCBPsInitialSystemProcess_EPROCESSpointerin_KTHREADImageFileNamein_EPROCESSX43AbortFactorsToolVirtualAddressTranslationinKernelSpaceGuessingOSversionandArchitectureGettingKernelObjectsVolatilityFramework2factors:_DISPATCHER_HEADERandImageFileName(PsIdleProcess)1factor:_DBGKD_DEBUG_DATA_HEADER642factors:_DBGKD_DEBUG_DATA_HEADER64andPsActiveProcessHeadMandiantMemoryze4factors:_DISPATCHER_HEADER,PoolTag,FlagsandImageFileName(PsInitialSystemProcess)2factors:_DISPATCHER_HEADERandoffsetvalueofImageFileName(PsInitialSystemProcess)NoneHBGaryResponderNone1factor:OperatingSystemVersionofkernelheader1factor:ImageFileName(PsInitialSystemProcess)Loadakerneldriverintox86XPVM–Thedrivermodifies1byteofthefollowingdataSizein_DISPATCHER_HEADERofPsIdleProcessPoolTagin_POOL_HEADERofPsInitialSystemProcessMajorOperatingSystemVersioninPEheaderofWindowskernelCheckthemodificationusingWinDbgAcquirethememoryimageusingLiveCloudKd[14]Analysisusingthreetools44DemousingPoCDriver(Video)IMPROVEMENTPLANS45GuessingbasedonaddressvaluesMinimumguessingSeparatingimplementationstogetkernelobjects46ImprovementPlansThemodificationofaddressvaluesoftencausesBSODorfunctionfailures–_EPROCESSobjectcarvingbyMemoryze–_KPCRobjectcarvingbyVolatilityFramework[15]47GuessingBasedonAddressValues_KPCRaddress==SelfPcrand_KPRCBaddress==PrcbSupportcrashdumpformat–Registervaluescannotbemodified48Minimumguessing(1)DataincrashdumpheaderExtractedfrom(Win32ddimplementation)AbortFactorDTBCR3registerOSversionnt!
NtBuildNumberXPAEenabledCR4registerPsActiveProcessHead_KDDEBUGGER_DATA64XPsLoadedModuleList_KDDEBUGGER_DATA64XSupportargumentpassingoptionsaboutDTBandOSversion–VolatilityFrameworksupportsthemspecifyOSversionbyusing"--profile"optionspecifyDTBvaluebyusing"--dtb"option49Minimumguessing(2)IfDTBvaluecannotbeacquired,displaytheresultminimally-extractedbyobjectcarving50SeparatingimplementationstogetkernelobjectsGettingtheseinformationdoesn'tneedDTBvalueWRAP-UP51Proposedantianalysismethodcanabortmemoryanalysistoolsbymodifyingonlyone-byte–ThemethodiseffectiveformemoryimagesofallOSversionsandarchitectures–Abouttheimpactontherunningsystem,longtermevaluationsmaybeneededIhope–Developersimprovetheimplementations–Usersfigureoutinternalsofmemoryanalysisanddealwithanalysiserrors52Wrap-up53Questions(twitter:@cci_forensics)PleasecompletetheSpeakerFeedbackSurveys!
[1]HBGaryFastDumpPro[2]EnCaseWinEn(build-intoolofEnCase)[3]MoonSolsWindowsMemoryToolkit[4]ReservedAddressSpaceinWindowsPhysicalMemory[5]VolatilityFramework[6]timelinerplugin[7]Update:MemoryForensicEnScript[8]MandiantRedline[9]MandiantMemoryze[10]"SHADOWWALKER"RaisingTheBarForRootkit[11]MeterpreterAntiMemoryForensics(Memoryze)Script[12]RobustSignaturesforKernelDataStructures[13]IdentifyingMemoryImages[14]YOURCLOUDISINMYPOCKET[15]FindingObjectRootsinVista(KPCR)54References
forsubmissionMemoryForensicsOverview–MemoryAcquisition–MemoryAnalysisPreviousWorks:AntiMemoryForensicsProposedAntiAnalysisMethodImprovementPlansWrap-upSummary2MEMORYFORENSICSOVERVIEW3Analyzingvolatiledataisimportanttodetectthreatsquickly–increasingamountsofdiskdata–antidiskforensicmethodsusedbymalwaresMemoryforensicsbecamepopularoverthelastfewyears2stepsformemoryforensics–memoryacquisitionandmemoryanalysis4What'sMemoryForensicsTargetMachineInvestigator'sMachineMemoryImageFile1.
AcquireRAMdataasanimagefile2.
ParseandanalyzetheimageofflineOfflineparsingamemoryimagedoesn'tusesystemAPIsMemoryforensicscanget–unallocateddata(e.
g.
,terminatedprocess)–datahiddenbymalware(e.
g.
,hiddenprocess)5WhyMemoryForensicsLiveResponseToolMemoryForensicAnalysisToolRunningProcessHiddenProcessTerminatedProcessAllocatedUnallocatedWindowsAPIParsebinaryimageandextractinformationfromitGetinformationthroughsystemAPIRawImageAcquisition–HBGaryFastDumpPro[1]–GuidanceWinEn[2]–MoonSolsWindd[3]CrashDumpImageAcquisition–MoonSolsWinddMemoryImageConversion–MoonSolsWindowsMemoryToolkit[3]6SomeFormats/AcquisitonToolsMemoryImageFileCPURegisterIncludedCrashDumpHibernationNotIncludedRawDifferencebetweenRawImageandCrashDumpCrashdumpfiledoesn'tinclude–1stPage–PagesreservedbydevicesRun[0]BasePage=0x1,PageCount=0x9eRun[1]BasePage=0x100,PageCount=0xeffRun[2]BasePage=0x1000,PageCount=0xeef0Run[3]BasePage=0xff00,PageCount=0x1001stPage(BIOSReserved)AddressSpaceReservedbyDevices(NotIncludedincrashdump)PhysicalMemoryAddressSpace(e.
g.
,256MBRAM)7EvaluationofMemoryAcquisitionToolsCanrawimageacquisitiontoolsget1stpageanddevice-reservedpages[4]–WinEn–Win32dd/c0MemoryContent(/c)option–Caution:/c0optionmaycauseBSODonx64machineWinEnFDProWin32dd/c0Win32dd/c1Win32dd/c21stPageDevicereservedpages8AnalysisExample:MakingObjectCreationTimeline9VolatilityFramework[5]–timelinerplugin[6]usedkernelobjects(process/thread/socket)eventlogsSpyEyebot(deadprocess)TCPconnectionestablishedbyexplorer.
exeCodeinjectionactivityAnalysisExample:DetectingCodeInjection10Detectingcodeinjection–VolatilityFrameworkmalfind–EnCaseEnScript[7]VadDump–MandiantRedline[8](GUIfront-endforMemoryze[9])ThetoolscheckprotectionflagofVirtualAddressDescriptorMandiantRedline(Memoryze)HBGaryResponderVolatilityFramework2.
0EnCaseEnScirptSupportedWindowsOSAllAllXP/Vista/7/2003/2008XP/7/2003/2008SupportedImageFormatRawRawRawCrashdumpHibernationRawCrashdumpSupportedCPUArchitectureIntelx86AMDx64Intelx86AMDx64Intelx86Intelx86AMDx64Extractingdeadprocess/closedconnectionNoNoYesYesNoteMalwareRiskIndex,MemD5DigitalDNA,codegraphingOpensource,richpluginsMultilingualsearch,EntropyComparisonofMemoryAnalysisTools11PREVIOUSWORKS:ANTIMEMORYFORENSICS12ShadowWalkerisproposedbySherriSparksandJamieButlertohidemaliciousmemoryregions–Installedpagefaulthandlermakesde-synchronizedDTLB/ITLBdataaccess->randomgarbagedataexecuteaccess->rootkitcodeMemoryacquisitiontoolscannotpreventShadowWalkerfromhidingmemorypages–ButAnalysistoolscandetecttheIDThooking13AntiAcquisitionMethods:ShadowWalker[10]Proofofconceptscript–killingspecifiedprocessesorpreventingdriverloadingswiththeaimofmemoryacquisitionfailureVeryeasytoimplement–Theevasionisalsoeasy(e.
g.
,randomname)–Preventingdriverloadingshasanimpactontherunningsystem14AntiAcquisitionMethods:MeterpreterAntiMemoryForensicsScript[11]Objectcarvingisonetechniquetoextractkernelobjectinformation–e.
g.
,processobject(_EPROCESS)PTFinder:Type/Sizein_DISPATCHER_HEADERVolatilityFramework:PoolTagin_POOL_HEADERBrendanDolan-Gavittetal.
warnedanattackercouldchangethevaluestohideaspecifiedobject[12]–Instead,theyproposedrobustsignaturescausingBSODorfunctionalityfailuresifthevaluesarechanged15AntiAnalysisMethod:AntiObjectCarvingmodifyingheadervaluesofcmd.
exeClosed-sourceanalysistoolscanfindthehiddenprocess–HowdotheyfinditOtherthanobjectcarving,thereareseveralkeyoperationsforanalyzingmemoryimage–TheoperationsarerobustLet'scheckit!
16AntiAnalysisMethod:AntiObjectCarving(Cont.
)MemoryzeHBGaryResponderPROPOSEDANTIANALYSISMETHOD17Researchedimplementationsofthreemajortools–VolatilityFramework2.
0–MandiantMemoryze2.
0–HBGaryResponderCommunityEdition2.
0Foundthreeoperationsexecutedinmemoryanalysisincludeafewunconsideredassumptions–Proposedmethodmodifiesone-byteofdatarelatedtotheoperationsThedataisdefinedas"AbortFactor"–Itcan'thidespecificobjects,butcanabortanalyses–NoimpactontherunningsystemNoBSOD,noerrorsforafewdaysto2weeks18AbstractofProposedMethodVirtualaddresstranslationinkernelspaceGuessingOSversionandArchitectureGettingkernelobjects–traversinglinkedlistsorbinarytrees–objectcarving19SensitiveThreeOperationsinMemoryAnalysisVirtualaddresstranslationinkernelspaceGuessingOSversionandArchitectureGettingkernelobjects–traversinglinkedlistsorbinarytrees–objectcarving20SensitiveThreeOperationsinMemoryAnalysisOSswitchesitscontextbyloadingDirectoryTableBase(DTB)ofeachprocess–DTBisstoredineachprocessobject(_EPROCESS)Initially,analysistoolsmustgetDTBvalueforkernelspaceTwoprocesseshavethekernelDTB–PsInitialSystemProcess(Systemprocess)–PsIdleProcess(Idleprocess)21VirtualAddressTranslationinKernelSpaceOSloadsDirectoryTableBase(Startphysicaladdressforaddresstranslation)intoControlRegister(CR3)x86AddressTranslation-HowPAEX86Workshttp://technet.
microsoft.
com/en-us/library/cc736309(WS.
10).
aspx22VirtualAddressTranslationinKernelSpace:ProcessObjectStructure_POOL_HEADER_OBJECT_HEADER_EPROCESS_KPROCESS_DISPATCHER_HEADERPoolTag:"Pro"TypeandSizeDTBImageFileName:"System"or"Idle"FlagsSearch_DISPATCHER_HEADERtoget_EPROCESSCheckwhethertheImageFileNameis"Idle"–IftheprocessisIdle,getDTBvaluein_KPROCESS23VirtualAddressTranslationinKernelSpace:VolatilityFramework_DISPATCHER_HEADER(e.
g.
,"x03x00x1bx00")ImageFileNameSearch"System"tofindImageFileNamein_EPROCESSofPsInitialSystemProcessValidatebyusing_DISPATCHER_HEADERinthe_KPROCESS–All_DISPATCHER_HEADERpatternsarechecked24VirtualAddressTranslationinKernelSpace:MandiantMemoryzeOSversion_DISPATCHER_HEADERByteSequenceXP32bit03001B00200332bit03001E00200364bit03002E00Vista32bit03002000Vista64bit03003000732bit03002600764bit03005800Validatebyusingthefollowingvalues–Flagsin_OBJECT_HEADERThedistancebetweenPoolTagand_EPROCESSiscalculatedaccordingtothevalue–PoolTagin_POOL_HEADERSearchPoolTagfrom_EPROCESSpositionandcheckwhetherthesearchhitoffsetisequaltothecalculateddistanceIfalldataisvalid,gettheDTBvalue25VirtualAddressTranslationinKernelSpace:MandiantMemoryze(Cont.
)Search_DISPATCHER_HEADERstoget_EPROCESSGetDTBvaluefromtheresultandvalidateitResponderseemstobeequippedwiththealgorithmguessingkernelDTB–IfDTBsofPsInitialSystemProcessandPsIdleProcessarenotfound,aguessedDTBvalueisused26VirtualAddressTranslationinKernelSpace:HBGaryResponder27VirtualAddressTranslationinKernelSpace:RelatedDataToolRelatedDataAbortFactorRemarksVolatilityFramework_DISPATCHER_HEADERXPsIdleProcessImageFileNamein_EPROCESSXMandiantMemoryze_DISPATCHER_HEADERXPsInitialSystemProcessPoolTagin_POOL_HEADERXFlagsin_OBJECT_HEADERXImageFileNamein_EPROCESSXHBGaryResponder_DISPATCHER_HEADERoriginalguessingalgorithmVirtualaddresstranslationinkernelspaceGuessingOSversionandArchitectureGettingKernelObjects–traversinglinkedlistsorbinarytrees–objectcarving28SensitiveThreeOperationsinMemoryAnalysisSizeanddefinitionofkerneldatastructuresdifferaccordingto–OSversion(e.
g.
,XPSP2/SP3,7SP0/SP1)–architecture(x86andx64)Allanalysistoolsguesstheversionusingdebugstructures29GuessingOSversionandArchitectureOSversion_EPROCESSsize(bytes)WindowsXPSP332bit0x260Windows7SP032bit0x2C0Windows7SP064bit0x4D0WindowsVistaSP232bit0x270WindowsVistaSP264bit0x3E830GuessingOSversionandArchitecture:DebugStructuresandKeyValues_KPCR_DBGKD_GET_VERSION64_KDDEBUGGER_DATA64KdVersionBlockDebuggerDataListHeaderCmNtCSDVersion_DBGKD_DEBUG_DATA_HEADER64OwnerTag:"KDBG"SizeKernBaseKernBasePrcbDataPsActiveProcessHeadPsLoadedModuleList_KPRCBCurrentThreadUsersmustspecifyOSversionandArchitecture–e.
g.
,--profile=WinXPSP2x86Iftheversionisunknown,imageinfocommandcanguessit–scan_DBGKD_DEBUG_DATA_HEADER64[13]31GuessingOSversionandArchitecture:VolatilityFrameworkOwnerTag:"KDBG"SizeSupposedlydetermineOSandarchitecturebasedon_DISPATCHER_HEADERValidatethembyusinganoffsetvalueofImageFileNamein_EPROCESS32GuessingOSversionandArchitecture:MandiantMemoryzeOSversionoffsetvalueofImageFileNameXP32bit0x174200332bitSP00x154200332bitSP1/SP20x164XP/200364bit0x268Vista32bit0x14CVista64bit0x238732bit0x16C7/200864bit0x2E0TrytotranslateavirtualaddressofThreadListHeadin_KPROCESS–Ifpossible,theOSversionandarchitecturearecorrectGetSPversionfromCmNtCSDVersionin_KDDEBUGGER_DATA6433GuessingOSversionandArchitecture:MandiantMemoryze(Cont.
)GetKernBasevalue–_DBGKD_GET_VERSION64or_KDDEBUGGER_DATA64ValidatethePEheadersignatures–DOSheader"MZ"andNTheader"PE"GetOSversion–OperatingSystemVersionsinOptionalHeadere.
g.
,Windows7–MajorOperatingSystemVersion=6–MinorOperatingSystemVersion=1Getmorespecificversion–TimeDataStampinFileheader34GuessingOSversionandArchitecture:HBGaryResponder35GuessingOSversionandArchitecture:RelatedDataToolRelatedDataAbortFactorRemarksVolatilityFramework_DBGKD_DEBUG_DATA_HEADER64XMandiantMemoryze_DISPATCHER_HEADERXPsInitialSystemProcessoffsetvalueofImageFileNameXThreadListHeadin_KPROCESSCmNtCSDVersionin_KDDEBUGGER_DATA64HBGaryResponderKernBasein_DBGKD_GET_VERSION64or_KDDEBUGGER_DATA64PEHeaderofWindowskernelPEheadersignatures"MZ"/"PE"OperatingSystemVersioninOptionalHeaderXTimeDataStampinFileHeaderVirtualaddresstranslationinkernelspaceGuessingOSversionandArchitectureGettingKernelObjects–traversinglinkedlistsorbinarytrees–objectcarving36SensitiveThreeOperationsinMemoryAnalysisTraversinglinkedlistsorbinarytrees–Generally,usespeciallead/rootaddressesPsActiveProcessHeadforprocesslistPsLoadedModuleListforkernelmodulelistVadRootforVirtualAddressDescriptortreeObjectcarving–Generally,usefixedvaluesinheaders_POOL_HEADER_DISPATCHER_HEADERMyresearchfocusedongetting_EPROCESS37GettingKernelObjectsProcesslististwo-waylink–Each_EPROCESSincludesActiveProcessLinks_LIST_ENTRY(FlinkandBlink)–PsActiveProcessHeadandPsInitialSystemProcessarebounduptogether38GettingKernelObjects:ProcessLinkedListPsActiveProcessHead_EPROCESS"System"_EPROCESS"smss.
exe"_EPROCESS"win32dd.
exe"FLINKBLINKFLINKBLINKFLINKBLINKFLINKBLINK.
.
.
.
.
.
.
.
.
Traversinglinkedlistsorbinarytrees–Search_DBGKD_DEBUG_DATA_HEADER64–getPsActiveProcessHeadin_KDDEBUGGER_DATA64Objectcarving–usePoolTagin_POOL_HEADER39GettingKernelObjects:VolatilityFrameworkExecutingKDBGScannerGetting_DBGKD_DEBUG_DATA_HEADER64(=_KDDEBUGGER_DATA64)addressObjectcarving–find_EPROCESSusingaddressvaluese.
g.
,–DTBis0x20-bytesaligned–(Peb&0x7ffd0000)==0x7ffd0000–(ActiveProcessLinks.
Flink&0x80000000)==0x80000000–similartorobustsignaturesproposedbyBrendanDolan-Gavittetal.
[12]40GettingKernelObjects:MandiantMemoryzeTraversinglinkedlistsorbinarytrees–getCurrentThreadin_KPRCB–get_EPROCESSfromthethreade.
g.
,ApcState.
Processin_KTHREAD(XP)–starttotraverseprocesslistfromthe_EPROCESS"System"stringiscomparedwithImageFileNameof_EPROCESS–foridentifyingPsActiveProcessHead–fordetectinghiddenprocess41GettingKernelObjects:HBGaryResponder42GettingKernelObjects:RelatedDataToolRelatedDataAbortFactorRemarksVolatilityFramework_DBGKD_DEBUG_DATA_HEADER64XPsActiveProcessHeadin_KDDEBUGGER_DATA64XPoolTagin_POOL_HEADERMandiantMemoryzeaddressvaluesin_EPROCESS(DTB,Peb,etc.
)HBGaryResponderCurrentThreadin_KPRCBPsInitialSystemProcess_EPROCESSpointerin_KTHREADImageFileNamein_EPROCESSX43AbortFactorsToolVirtualAddressTranslationinKernelSpaceGuessingOSversionandArchitectureGettingKernelObjectsVolatilityFramework2factors:_DISPATCHER_HEADERandImageFileName(PsIdleProcess)1factor:_DBGKD_DEBUG_DATA_HEADER642factors:_DBGKD_DEBUG_DATA_HEADER64andPsActiveProcessHeadMandiantMemoryze4factors:_DISPATCHER_HEADER,PoolTag,FlagsandImageFileName(PsInitialSystemProcess)2factors:_DISPATCHER_HEADERandoffsetvalueofImageFileName(PsInitialSystemProcess)NoneHBGaryResponderNone1factor:OperatingSystemVersionofkernelheader1factor:ImageFileName(PsInitialSystemProcess)Loadakerneldriverintox86XPVM–Thedrivermodifies1byteofthefollowingdataSizein_DISPATCHER_HEADERofPsIdleProcessPoolTagin_POOL_HEADERofPsInitialSystemProcessMajorOperatingSystemVersioninPEheaderofWindowskernelCheckthemodificationusingWinDbgAcquirethememoryimageusingLiveCloudKd[14]Analysisusingthreetools44DemousingPoCDriver(Video)IMPROVEMENTPLANS45GuessingbasedonaddressvaluesMinimumguessingSeparatingimplementationstogetkernelobjects46ImprovementPlansThemodificationofaddressvaluesoftencausesBSODorfunctionfailures–_EPROCESSobjectcarvingbyMemoryze–_KPCRobjectcarvingbyVolatilityFramework[15]47GuessingBasedonAddressValues_KPCRaddress==SelfPcrand_KPRCBaddress==PrcbSupportcrashdumpformat–Registervaluescannotbemodified48Minimumguessing(1)DataincrashdumpheaderExtractedfrom(Win32ddimplementation)AbortFactorDTBCR3registerOSversionnt!
NtBuildNumberXPAEenabledCR4registerPsActiveProcessHead_KDDEBUGGER_DATA64XPsLoadedModuleList_KDDEBUGGER_DATA64XSupportargumentpassingoptionsaboutDTBandOSversion–VolatilityFrameworksupportsthemspecifyOSversionbyusing"--profile"optionspecifyDTBvaluebyusing"--dtb"option49Minimumguessing(2)IfDTBvaluecannotbeacquired,displaytheresultminimally-extractedbyobjectcarving50SeparatingimplementationstogetkernelobjectsGettingtheseinformationdoesn'tneedDTBvalueWRAP-UP51Proposedantianalysismethodcanabortmemoryanalysistoolsbymodifyingonlyone-byte–ThemethodiseffectiveformemoryimagesofallOSversionsandarchitectures–Abouttheimpactontherunningsystem,longtermevaluationsmaybeneededIhope–Developersimprovetheimplementations–Usersfigureoutinternalsofmemoryanalysisanddealwithanalysiserrors52Wrap-up53Questions(twitter:@cci_forensics)PleasecompletetheSpeakerFeedbackSurveys!
[1]HBGaryFastDumpPro[2]EnCaseWinEn(build-intoolofEnCase)[3]MoonSolsWindowsMemoryToolkit[4]ReservedAddressSpaceinWindowsPhysicalMemory[5]VolatilityFramework[6]timelinerplugin[7]Update:MemoryForensicEnScript[8]MandiantRedline[9]MandiantMemoryze[10]"SHADOWWALKER"RaisingTheBarForRootkit[11]MeterpreterAntiMemoryForensics(Memoryze)Script[12]RobustSignaturesforKernelDataStructures[13]IdentifyingMemoryImages[14]YOURCLOUDISINMYPOCKET[15]FindingObjectRootsinVista(KPCR)54References
妮妮云香港CTG云服务器1核 1G 3M19元/月
香港ctg云服务器香港ctg云服务器官网链接 点击进入妮妮云官网优惠活动 香港CTG云服务器地区CPU内存硬盘带宽IP价格购买地址香港1核1G20G3M5个19元/月点击购买香港2核2G30G5M10个40元/月点击购买香港2核2G40G5M20个450元/月点击购买香港4核4G50G6M30个80元/月点击购买香...
湖北50G防御物理服务器( 199元/月 ),国内便宜的高防服务器
4324云是成立于2012年的老牌商家,主要经营国内服务器资源,是目前国内实力很强的商家,从价格上就可以看出来商家实力,这次商家给大家带来了全网最便宜的物理服务器。只能说用叹为观止形容。官网地址 点击进入由于是活动套餐 本款产品需要联系QQ客服 购买 QQ 800083597 QQ 2772347271CPU内存硬盘带宽IP防御价格e5 2630 12核16GBSSD 500GB30M1个IP...
ucloud香港服务器优惠活动:香港2核4G云服务器低至358元/年,968元/3年
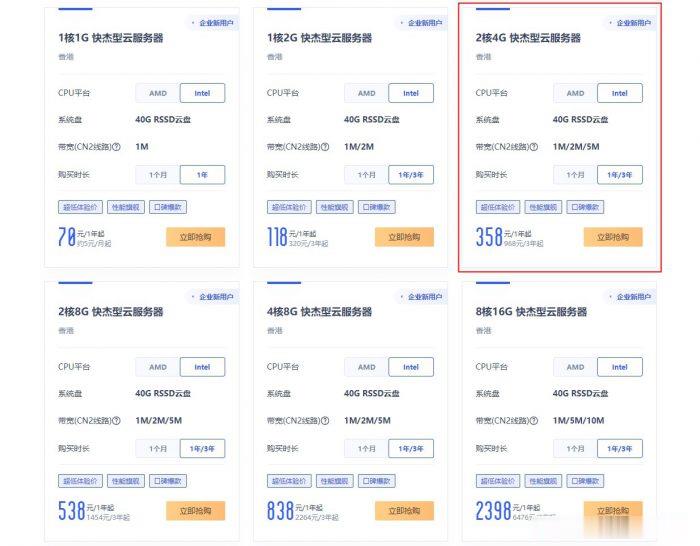
ucloud香港服务器优惠降价活动开始了!此前,ucloud官方全球云大促活动的香港云服务器一度上涨至2核4G配置752元/年,2031元/3年。让很多想购买ucloud香港云服务器的新用户望而却步!不过,目前,ucloud官方下调了香港服务器价格,此前2核4G香港云服务器752元/年,现在降至358元/年,968元/3年,价格降了快一半了!UCloud活动路子和阿里云、腾讯云不同,活动一步到位,...
spaceos为你推荐
-
www.hao360.cn主页设置为http://hao.360.cn/,但打开360浏览器先显示www.yes125.com后转换为www.2345.com,搜索注册表和bbs.99nets.com送点卷的冒险岛私服百度关键词价格查询百度关键字如何设定竟价价格?xyq.163.cbg.comhttp://xyq.cbg.163.com/cgi-bin/equipquery.py?act=buy_show_equip_info&equip_id=475364&server_id=625 有金鱼贵吗?www.gegeshe.com有什么好听的流行歌曲百度指数词百度指数是指,词不管通过什么样的搜索引擎进行搜索,都会被算成百度指数吗?ww.66bobo.com谁知道11qqq com被换成哪个网站www.15job.com广州天河区的南方人才市场www.bbbb.com二级域名怎么申请?看URL怎么分辨出二级域名、三级域名4399宠物连连看2.5我怎么找不到QQ里面的宠物连连看呢