权限动网先锋论坛-『 web开发讨论区 』-针对sql injection的sql server安全设置初级篇(Mobile pioneer Forum - Web Development Forum - for SQL Injection´s SQL Server Security Settings)
动网先锋论坛- 『 web开发讨论区』 -针对sql injection的sqlserver安全设置初级篇Mobile pioneer Forum-Web DevelopmentForum - for SQL Injection' s SQL Server Security SettingsMobile pioneer Forum - "WEB Development Forum" - for SQLINJECTION' s SQL SERVER security settings
Collect this page
Contact us
Forum Help
Qmtxf re login, stealth user control panel, SMS search style,forum status, forum exhibition, props center exit
Website development, database development exchange, variousWEB development technology exchange, base camp, my inbox (0)Mobile network pioneer Forum - computer technology - "WEBDevelopment Forum" - for SQL INJECTION SQL SERVER securitysettings junior article
You are the 1369th person reading this post AP
* posting theme: initial article on security settings for SQLINJECTION' s SQL SERVER
Jadesun
Title: people don't want to say
Class: VIP
Article: 1338
Points: 2527
Registration: 2000-7-31
The landlord
For SQL INJECTION SQL SERVER security settings junior articleThe day before the SQL INJECTION attack testing intensified,many large websites and forums have been injected. These sitesgenerally use more than SQL
SERVER database, and because of this, many people begin to doubtthe security of SQL SERVER. Actually, SQL SERVER
2000 has passed the U.S. government' s C2 level securitycertification - this is the industry can have the highestcertification level, so the use of SQL
SERVER is pretty safe. Of course, there is still a gap betweenORCAL and DB2, but SQL
The ease of use and universality of SERVER can still be a reasonfor us to continue using it. How can you make the SQL SERVERsettings reassuring?
The first step must be to hit SQL
SERVER' s latest security patch, and now the patch is out of SP3.Download address:http://www.microsoft.com/sql/downloads/2000/sp3.asp. If thisstep is not done well, then we do not have the necessary tocont inue.
The second step is to modify the default 1433 port andhide theSQL SERVER. This prevents attempts to enumerate existing SQLServer on the network
The broadcast sent by the client responds. In addition, youneedto screen the 1433 port from the TCP/IP filter and hide yourSQL as much as possible
SERVER database. This way, but let the attack create SQLSERVER accounts can not immediately use the query analyzerremote login for the next attack. From the ASP, PHP and otherpages to construct malicious statements, there is also need tocheck the return value of the problem, than the direct queryanalyzer to benefit from the fall. So the first thing we needto do even let others into, nor allow an attacker to do nextsmoothly. Modification method: Enterprise Manager
Taking your database group-- >attributes-->-->-->TCP/IP- > conventional network configuration attributes
Here, modify your default port and hide the SQL SERVER.
The third step is an important step, and SQL INJECTION tendsto be in WEB
Generated in CODE. As a system administrator or databaseadministrator, you can't always look at each piece of code. Evenif we often look at the code, we can not guarantee our negligenceon the above. What can we do?We' ll start with the database roleto get the database users' rights to the lowest point. SQLSERVER' s default permissions are really a headache, very highpermissions, no permissions, and nothing to do, SYSADMIN anddb_owner is really a love and hate. An attacker, however,confirmed that the site had SQL
INJECTION vulnerability, there must be a step in the processof testing the site' s SQL SERVER users have much authority.Usually with the help of SELECT
IS_SRVROLEMEMBER (' sysadmin' ) , or SELECT IS_MEMBER
('db_owner' ) , or user
= 0 (compare characters with numbers, SQL
The SERVER will prompt the error message, which can be used totest some sensitive information, and so on. And, I dare not saymore. One is afraid of being wrong, and the other is afraid ofthe people in the alliance. At present, if the database userof the web site uses SA privileges, plus the absolute path ofthe WEB, the OVER of your website is declared. Db_ownerpermissions are the same. If the absolute path is confirmed,there is a 50% chance to give WEB in your machine
A Trojan horse, such as Haiyang. So here we've got a point. Wehave to create our own privileges so that the attacker can'tfind a place to go. Quote a SQL here
Examples of SERVER online help:
Method for creating SQL Server database roles (EnterpriseManager)
Create SQL Server database roles
1. expand the server group, and then expand the server.
2. expand the database folder, and then expand the databasewhere you want to create the roles.
3. right click on roles, and then click new database roles.
4. enter the name of the new role in the name box.
5. click Add to add members to the standard roles list, and thenclick one or more users you want to add. (optional)
Only users in the selected database can be added to the role.Object permission
A class of permissions that is called object permissions whenprocessing data or executing procedures:
? SELECT, INSERT, UPDATE, and DELETE statement permiss ions,which can be applied to the entire table or view.
SELECT and UPDATE statement permissions, which can beselectively applied to a single column in a table or view.SELECT permissions, which can be applied to user-definedfunctions.
INSERT and DELETE statement permissions that affect entire rows,sotheycanonlybeappliedtotables orviews, not to individualcolumns.
EXECUTE statement permissions, which can affect storedprocedures and functions.
Statement permission
The activities involved in creating items in a database ordatabase, such as tables or stored procedures, require anotherclass of permissions called statement rights. For example, ifa user must be able to create a table in the database, the usershould be granted it
CREATE TABLE statement permissions. Statement permissions(such as CREATE, DATABASE) apply to the statement itself,rather than to specific objects defined in the database.Statement authority:
? BACKUP DATABASE
? BACKUP LOG
? CREATE DATABASE
? CREATE DEFAULT
? CREATE FUNCTION
? CREATE PROCEDURE
·创建规则
·创建表
·创建视图
暗示性权限
暗示性权限控制那些只能由预定义系统角色的成员或数据库对象所有者执行的活动。例如 固定服务器角色成员自动继承在SQLsysadmin
服务器安装中进行操作或查看的全部权限。
数据库对象所有者还有暗示性权限可以对所拥有的对象执行一切活动。例如拥有表的用户可以查看、添加或删除数据更改表定义或控制允许其他用户对表进行操作的权限。d b_o wn e r在数据库中有全部权限。
db_accessadmin可以添加或删除用户ID。db_securityadmin可以管理全部权限、对象所有权、角色和角色成员资格。db_ddladmin可以发出所有DDL但不能发出格兰特、撤销或否认语句。db_backupoperator可以发出DBCC、检查站和备份语句。db_datareader可以选择数据库内任何用户表中的所有数据。db_datawri ter可以更改数据库内任何用户表中的所有数据。db_denydatareader不能选择数据库内任何用户表中的任何数据。db_denydatawriter不能更改数据库内任何用户表中的任何数据。在这儿把新建的数据库角色的权限配置好比如需要使用哪个表、视图、存储过程等。然后把db_owner和db_securityadmin、db_backupoperator取消不给攻击者备份
和创建数据库
表的机会一但攻击者具有这两个权限那么你的网站就还处在十分危险的状态。还有注意一下在创建数据库账号时千万不能对服务器角色进行选择。
第四步是修改内置存储过程SQL SQL Server。
服务器估计是为了安装或者其它方面它内置了一批危险的存储过程。能读到注册表信息能写入注册表信息能读磁盘共享信息等等. . . . . .各位看到这儿心里可能会在想我的网站中有其它的代码又不像查询分析器那样能查接将结果输出。给你这个权限又不能怎么样还是看不到信息。如果各位这样想就大错特错了提示一下如果攻击者有创建。
表的权限那么创建一个临时表然后将信息插入到表中然选择出来接着跟数字进行比较让SQL
服务器报错那么结果就全出来了. . . . . .所以我们要报着宁错杀不放过的态度进行修补。
先来列出危险的内置存储过程xp_cmdshellxp_regaddmultistringxp_regdeletekeyxp_regdeletevaluexp_regenumkeysxp_regenumvaluesxp_regreadxp_regremovemult istring
- 权限动网先锋论坛-『 web开发讨论区 』-针对sql injection的sql server安全设置初级篇(Mobile pioneer Forum - Web Development Forum - for SQL Injection´s SQL Server Security Settings)相关文档
- 论坛南方动漫网论坛管理办法
- 设置动网论坛基本设置教程
- 版主南方网动漫论坛管理制度
- 键入抓取动网论坛 Email 地址的一段代码源码精华教程
- 信息技术浅谈“动网论坛”在高中信息技术课堂中的应用
- 您的动网论坛前台使用手册_ASP_82.
RAKsmart裸机云/云服务器/VPS全场7折,独立服务器限量秒杀$30/月起
适逢中国农历新年,RAKsmart也发布了2月促销活动,裸机云、云服务器、VPS主机全场7折优惠,新用户注册送10美元,独立服务器每天限量秒杀最低30.62美元/月起,美国洛杉矶/圣何塞、日本、香港站群服务器大量补货,1-10Gbps大带宽、高IO等特色服务器抄底价格,机器可选大陆优化、国际BGP、精品网及CN2等线路,感兴趣的朋友可以持续关注下。裸机云新品7折,秒杀产品5台/天优惠码:Bare-...

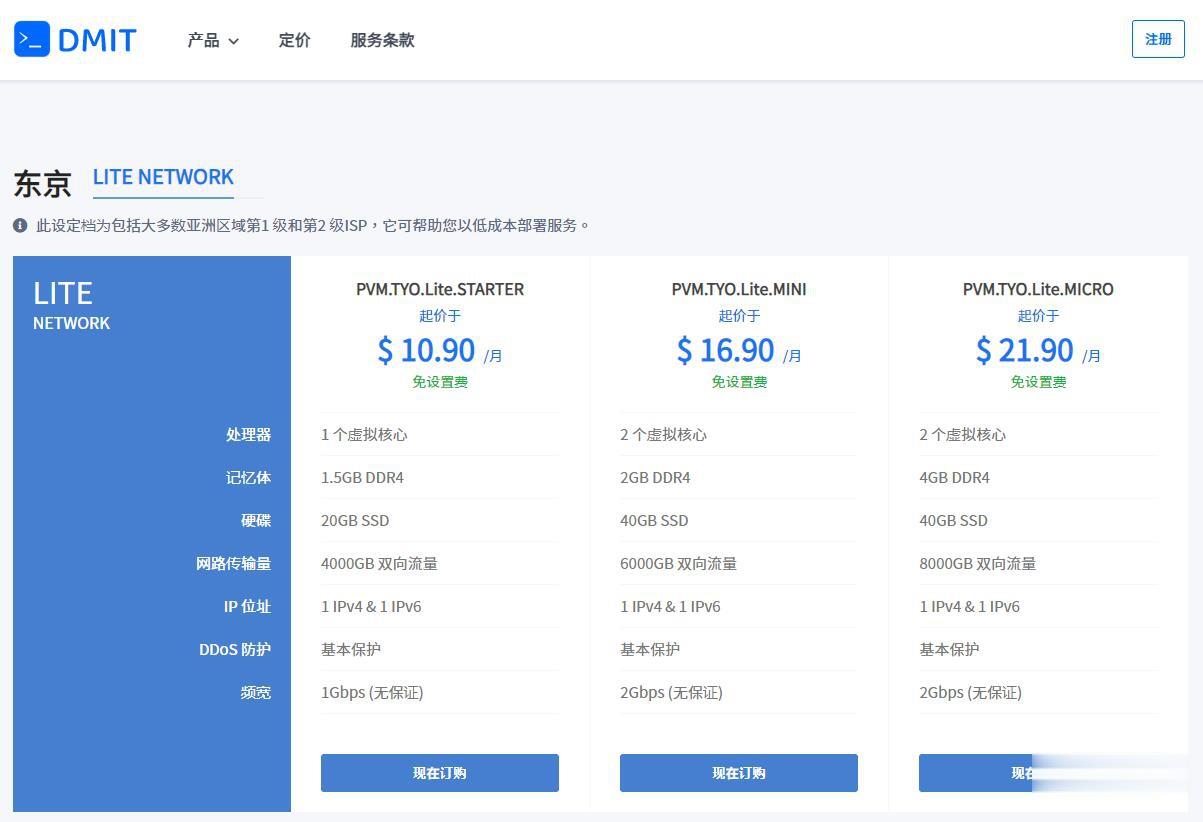
DMIT$10.9/月,日本VPS/三网直连/1核1.5G内存/20GB存储/1Gbps端口
优惠码年付一次性5折优惠码:TYO-Lite-Open-Beta-1y-50OFF永久8折优惠码:TYO-Lite-Open-Beta-Recur-20OFF日本vpsCPU内存SSD流量带宽价格购买1核1.5G20 GB4 TB1Gbps$10.9/月购买2核2 G40 GB6 TB1Gbps$16.9/月购买2核4 G60 GB8 TB1Gbps$21.9/月购买4核4 G80 GB12 TB...
vdsina:俄罗斯VPS(datapro),6卢布/天,1G内存/1核(AMD EPYC 7742)/5gNVMe/10T流量
今天获得消息,vdsina上了AMD EPYC系列的VDS,性价比比较高,站长弄了一个,盲猜CPU是AMD EPYC 7B12(经过咨询,详细CPU型号是“EPYC 7742”)。vdsina,俄罗斯公司,2014年开始运作至今,在售卖多类型VPS和独立服务器,可供选择的有俄罗斯莫斯科datapro和荷兰Serverius数据中心。付款比较麻烦:信用卡、webmoney、比特币,不支持PayPal...
-
软银亏损65亿美元马云仅仅持有阿里8.9%的股份,就有270多亿美元,孙正义的软银占有那么多股份,怎么还不是亚洲首富英语词典哪个好英语词典哪种更好啊?无纺布和熔喷布口罩哪个好一次性口罩的熔喷布和KN95的熔喷布有什么不同?美国国际东西方大学出国留学,美国“野鸡大学”有哪些?51空间登录以前的51空间怎么进?dns服务器未响应电脑上不了网了,显示DNS服务器未响应,什么意思360云盘360云盘干什么用的?360云盘企业版360云盘转企业版我的数据该怎么办360云盘论坛360云盘,百度云盘,115云盘,哪个好用一点,理由是什么月抛隐形眼镜月抛隐形眼镜大概多少钱