typespartnersonline
partnersonline 时间:2021-03-19 阅读:()
87Chapter7ANewSecurityArchitecturetoImproveBusinessAgilityRealityandRhetoricAnorganization'sabilitytolearn,andtranslatethatlearningintoactionrapidly,istheultimatecompetitiveadvantage.
—JackWelchSomeStarTrekepisodesfeaturesuspense-filledbattlesinwhichadversariesusesophisticatedphase-shiftingweaponsthatcanberapidlyadjusteduntiltheyfindawaytopenetratestaticforce-fielddefenses.
Forabeleagueredstarship,theonlyeffectiveresponseistousesimilarlyadaptableandfast-changingshields.
Asinformationsecurityprofessionals,wealsoneedextremelyagiledefensesthatcanbequicklyadaptedtomeetnewdemands.
Attackersarecontinuallyadapting,anddefendersalsoneedtocontinuallyadapt.
Butrapidlyevolvingthreatsareonlypartofthechallenge.
ThetechnologylandscapeischangingjustasfastduetotrendslikeITconsumerization.
AsIntel'sinformationriskandsecuritygroupconsidersthefuture,werealizethatweneedtoradicallychangeourapproachinordertofacethechallengesaheadandsupporttheProtecttoEnablemission.
Weneedamoreagilesecurityarchitecturethatcanquicklylearnandadapttonewchallengesastheyemerge.
Becausetheenvironmentischangingsoquickly,inwayswecannotcontrol,it'simpossibletopredictallthefuturechallengeswe'llneedtoface.
Weneedanarchitecturethatcanlearntomanagewhatwedon'tknow.
Thisflexibilitywillhelpthebusinessmovemorequickly,byenablingustorapidlyadoptnewtechnologiesandemergingusagemodelswhilecontinuingtoprovidesecurityintheever-evolvingthreatlandscape.
Alearningsystemishardertodefeatbecauseitcanmorequicklyadaptinresponsetonewattacks.
Afterintensebrainstormingsessions,ourinformationriskandsecurityteamdevisedanewsecurityarchitecture.
ThisarchitectureisourimplementationoftheProtecttoEnablestrategy.
Inthischapter,I'llprovideahigh-leveloverviewofthearchitectureanddescribehowitmeetssomekeysecuritychallenges.
ThoughtheoverviewisbasedonourworkatIntel,IbelievethatthisisanovelapproachtoenterprisesecuritythatmaybevaluableChapter7ANewSecurityArchitecturetoImproveBusinessAgility88tomanyotherorganizationsfacingtheseuniversalchallenges.
Myconversationswithpeersatothercompanieshavevalidatedthisview.
Manyofthemareconsideringsimilarstrategiesandinsomecaseshavebegunimplementingthem.
WeareimplementingthisarchitectureacrossIntel'sITenvironmentinaradicalfive-yearredesignofourinformationsecuritytechnology.
Evenwhiletheimplementationisinprogress,thenewarchitecturehasalreadydeliveredresultsbyhelpingusprovideinnovativesolutionstochallengingusecaseswhileactuallyreducingrisk.
IntelIThaspublishedmoredetaileddescriptionscoveringseveralaspectsofthearchitecture(Ben-Shalometal.
2011,SunderlandandChandramouly2011,Gutierrezetal.
2012),andweexpecttocontinuetopublishinformationinthefuture.
Akeyaspectofthearchitectureisthatitprovidesmoreflexible,dynamic,andgranularsecuritycontrolsthantraditionalenterprisesecuritymodels.
Thishelpsusaccommodateusagemodelssuchasbring-your-own-device(BYOD).
Wecanprovideuserswithdifferentlevelsofaccessdependingonfactorssuchasthedevicestheyareusingandtheirlocation.
Toachievethis,thetechnologydynamicallyadjustsauser'saccessprivilegesasthelevelofriskchanges.
Forexample,anemployeeshouldhavemorelimitedaccesstooursystemswhenusingaless-securedevicethanwhenusingahardened,fullymanagedenterprise-classsystem.
Thenewarchitecturegreatlyimprovesthreatmanagement.
Asnewrisksappear,weneedtobeabletoquicklyrecognizewhichoneswecanmitigate,learnasmuchaswecan,andtakeactionasquicklyaspossible.
AtIntel,weusemanyinformationsourcestogainanunderstandingoftherisks.
Collectively,thesesourcesprovideacontinuousfeedofcollectiveintelligencethatwecanusetolearn,adapt,andevolve.
AsIdescribedinChapter6,weuseemergingthreatanalysistohelpusanticipatefuturerisks.
Butourarchitecturealsoassumesthatcompromiseisinevitableandfocusesheavilyonsurvivability.
Weareapplyingsecuritymonitoringandbusinessintelligencetoanalyzepatternsofbehavioranddetectanomaliesthataresymptomsofattacks.
Withthisknowledge,wecanfurtherinvestigateandapplymitigationwherenecessary.
Inthefuture,thisapproachcouldbeextendedbyautomaticallytakingcorrectiveactionwhereitmakessensetodoso.
BusinessTrendsandArchitectureRequirementsBeforedivingintothespecificsofthearchitecture,I'llrecapsomeofthekeybusinessandtechnologytrends,focusingonhowtheydrivetheneedforspecificcapabilitiesinsecuritytechnology.
ITConsumerizationAsIdiscussedinChapter5,consumerizationisamajorITthemewithever-broadeningimpact.
Itincludesseveraltrends,includingtheadoptionofnewapplicationsandsupportforconsumerdevices.
ManyofIntel'shighlymobileemployeeswanttousetheirownconsumerdevices,suchassmartphonesandtablets,forwork.
Thisincreasesproductivitybyenablingemployeestocollaborateandaccessinformationfromanywhere,atanytime.
TosupportChapter7ANewSecurityArchitecturetoImproveBusinessAgility89this,weprovideaccesstocorporatee-mailandotherapplicationsfromemployee-ownedsmartphonesandtablets.
Somepeoplebelievethatinthefuture,alldeviceswillbeconsumer-owned,andthatenterpriseswillnolongerpurchasedevicesfortheirusers.
Ibelievethismightbethecaseinsomeworkenvironments,butIdoubtthatitwillsuitallorganizations.
Foracompanyprovidingcallcenterservices,withmostemployeesworkingfromhome,itmightmakesensethatemployeesexclusivelyusetheirownpersonalsystemsforwork.
Butthisstrategywouldbemoreriskyforafinancialservicescompanywhoseemployeeshandlehighlysensitiveinformationthat'ssubjecttoextensiveregulatoryrequirements.
Nevertheless,theconsumerizationtrendcontinuestogrowatIntelandotherorganizations.
Accordingly,we'llneedtoprovideemployeeswithalevelofaccesstoIntelresourcesfromanexpandingcontinuumofclientdevices,someofwhichhavemuchweakersecuritycontrolsthantoday'senterpriseclients(seesidebar).
CONSUMERIZINGENTERPRISEITAND"ENTERPRISING"THECONSUMERDiscussionsofITconsumerizationtendtodrawaclearlinebetweenbusinessdevicesthatcanbemanagedandtrusted,andpersonalconsumerdevicesthatareessentiallyunmanagedanduntrusted.
However,notallconsumerdevicesarecreatedequal.
Fromasecuritystandpoint,itmaybemorevaluabletothinkaboutadevice'scapabilitiesthantocategorizeitbasedsolelyonwhetherit'smarketedasanenterprisedeviceorapersonaldevice.
Thesecurityofadevicedependsontheinherentfeaturesofthehardware,operatingsystem,andapplications,andonwhetheritenablesustoaddfurthersecurityandmanageabilitycapabilitiesthatmitigatetherisksofenterpriseuse.
Asthevarietyofconsumerdevices,suchassmartphones,continuestoexpand,usersmaychoosefromdozensofmodelswithdifferentlevelsofsecuritycapabilities.
GreatersecurityandmanageabilitymeansthatITcanplacegreatertrustinthedeviceandprovideacorrespondinglygreaterlevelofaccesstoenterpriseresources.
Extendingthisideafurther,theinformationsecuritygroupcouldevaluatethesecurityofavailableconsumerdevicesandprovideguidanceaboutthelevelofenterpriseaccessthatuserswillbeallowedwitheachdevice.
Usersmayprefertobuyamoresecuredevicebecauseitwillprovidethemmoreaccess.
Withgreateraccess,theycanusethedeviceformoreoftheirdailyworkactivities.
Thisabilityinturnenablesthemtobemoreproductive.
Atthesametime,employeesincreasinglyexpecttohaveavailabletothematworkthetypesofconsumerservicesandcloudapplicationsthattheyuseintheirpersonallives.
Theseincludesocialcomputingapplicationssuchasblogsandwikis,video-sharingsites,andfile-sharingservices.
Chapter7ANewSecurityArchitecturetoImproveBusinessAgility90Weneedasecurityarchitecturethatenablesustomorequicklysupportnewdevicesandprovideaccesstoagreaterrangeofapplicationsanddata,withoutincreasingrisk.
Weneedtobeabletodynamicallyadjustthelevelsofaccessweprovideandthemonitoringweperform,dependingonthesecuritycontrolsoftheclientdevice.
NewBusinessNeedsNearlyallcompaniesnowrelyonagrowingnetworkofbusinesspartners,andconductmanyoftheirinteractionswiththosepartnersonline.
Intelisnoexception—wearedevelopinganincreasingnumberofsystemsforonlinecollaborationwithbusinesspartners.
Also,likemanycompanies,Intelisexpandingintonewmarketsthroughbothorganicgrowthandacquisitions.
Becauseofthesebusinesstrends,mostorganizationsneedtoprovideaccesstoabroaderrangeofusers,manyofwhomarenotemployees.
Manyalsoneedtobeabletosmoothlyintegrateacquiredcompaniesandprovidethemwithaccesstoresources.
Ingeneral,weneedtoquicklyprovidenewusersaccesswhileminimizingriskandprovidingselective,controlledaccessonlytotheresourcestheyneed.
CloudComputingMostorganizationsarealreadyusingcloudservicesinsomeformtoachievebenefitssuchasgreateragilityandlowercost.
Likemanycompanies,IntelITisimplementingaprivatecloudbasedonvirtualizedinfrastructure,andwearealsousingexternalcloudservicesfornoncriticalapplications.
Inthefuture,weexpectgreateruseofhybridcloudsthatusebothinternalandexternalresources.
ThistrendmeansthatITservicesatmanyorganizationswillbeprovidedbyamixtureoftraditionalandcloud-basedinternalandexternalservices.
Duringatypicalday,employeesmayaccessavarietyofdifferentservices,someofwhichareinternalandsomeexternal.
Ultimately,theyshouldbeabletoeasilymovebetweentheseserviceswithoutneedingtologinmultipletimesorevenknowwheretheservicesarelocated.
Securingaccesstocloud-basedservicespresentschallengesthataren'teasilyaddressedusingconventionalsecuritycontrols.
Incloudenvironments,systemsandtheirdataarevirtualizedandmaymigratedynamicallytodifferentnetworklocations.
Thismakesitdifficulttoeffectivelyrestrictaccessusingtraditionalsecuritycontrolssuchasfirewalls,whichrelyonfixedlocationsofsystemsandamorestaticnatureofthedata.
Weneedmuchmoregranularanddynamiccontrolsthatarelinkedtotheresourcesthemselvesratherthanjusttheirnetworklocation.
ChangingThreatLandscapeThethreatlandscapeisevolvingrapidly.
Increasingly,attackersaretakingastealthyapproach,creatingmalwarethatquietlygainsaccessandattemptstoremainundetectedinordertomaintainaccessovertime.
Asthenumberofthreatsincreasesandnewtypesofmalwareemerge,weneedtoassumethatcompromiseisinevitable.
Chapter7ANewSecurityArchitecturetoImproveBusinessAgility91Traditionalenterprisesecurityarchitectureshavereliedlargelyonpreventativecontrolssuchasfirewallslocatedatthenetworkperimeter.
However,ourprimaryfocushasshiftedtoprovidingcontrolledaccesstoabroaderrangeofusersanddevices,ratherthansimplypreventingaccess.
Inaddition,thecontinuallychangingthreatlandscapemakesitnecessarytoassumethatcompromisewilloccur.
Onceattackershavegainedaccesstotheenvironment,thepreventativecontrolstheyhavebypassedareworthless.
Althoughtheseperimetercontrolswillcontinuetohavesomevalue,weneedtoolsthatincreasetheabilitytosurviveandrecoveronceattackershavegainedaccesstotheenvironment.
PrivacyandRegulatoryRequirementsThegrowingemphasisonprivacyrequirementsandtheincreasinglycomplexregulatoryenvironmenthavemanyimplicationsforthewaywemanageinformation.
Someregulationscreatetheneedformorecontroloverwhereinformationisstoredandrequirespecificlevelsofprotectionandtracking.
Ourarchitecturemustprovidethisassurance,allowingustobuildahigh-securityenvironmentandaccesscontrolsappropriatefortheprotectionofhighlyregulatedinformation.
NewArchitectureTomeettheserapidlychangingrequirements,weneedahighlyflexibleanddynamicarchitecture.
Thearchitectureshouldenableustomorequicklyadoptnewdevices,usemodels,andcapabilities;providesecurityacrossanincreasinglycomplexenvironment;andadapttoachangingthreatlandscape.
AtIntel,weformedateamcharteredwithdesigningthisarchitecturefromscratch,takingafreshapproachtoenterprisesecurity,thendetermininghowtoimplementthisnewarchitectureacrossourexistingITenvironment.
Keygoalsincludehelpingincreaseemployeeproductivitywhilesupportingnewbusinessrequirementsandtechnologytrends,includingITconsumerization,cloudcomputing,andaccessbyabroaderrangeofusers.
Atthesametime,thearchitectureisdesignedtoreduceourattacksurfaceandimprovesurvivability—evenasthethreatlandscapegrowsincomplexityandmaliciousness.
Thearchitecturemovesawayfromthetraditionalenterprisetrustmodel,whichisbinaryandstatic.
Withthistraditionalmodel,auserisingeneraleithergrantedordeniedaccesstoallresources;oncegranted,thelevelofaccessremainsconstant.
Thenewarchitecturereplacesthiswithadynamic,multitieredtrustmodelthatexercisesmorefine-grainedcontroloveridentityandaccesscontrol,includingaccesstospecificresources.
Thismeansthatforanindividualuser,thelevelofaccessprovidedmayvarydynamicallyovertime,dependingonavarietyoffactors—suchaswhethertheuserisaccessingthenetworkfromahighlysecuremanageddeviceoranuntrustedunmanageddevice.
Thearchitecture'sflexibilityallowsustotakeadvantageoftrustthat'sbuiltintodevicesatahardwarelevel,aswellastrustinapplicationsandservices.
Increasingly,deviceswillincludehardware-enforcedsecuritydesignedtoensuretheintegrityoftheapplicationsanddataonthedevice.
ThearchitecturetakesthisintoaccountwhenChapter7ANewSecurityArchitecturetoImproveBusinessAgility92determiningwhethertoallowaccesstospecificresources—amore-trustedplatformcanbeallowedgreateraccessthanaless-trustedone.
Thearchitectureisbasedonfourcornerstones:TrustCalculation.
Thisuniqueelementofthearchitecturehandlesuseridentityandaccessmanagement,dynamicallydeterminingwhetherausershouldbegrantedaccesstospecificresourcesand,ifso,whattypeofaccessshouldbegranted.
Thecalculationisbasedonfactorssuchastheuser'sclientdeviceandlocation,thetypeofresourcesrequested,andthesecuritycontrolsthatareavailable.
SecurityZones.
Theinfrastructureisdividedintomultiplesecurityzonesthatprovidedifferentlevelsofprotection.
Theserangefromtrustednetworkzonescontainingcriticaldata,withtightlycontrolledaccess,tountrustedzonescontainingless-valuabledataandallowingbroaderaccess.
Communicationbetweenzonesiscontrolledandmonitored;thishelpsensureuserscanonlyaccesstheresourcesforwhichtheyhavebeenauthorizedandpreventscompromisesfromspreadingacrossmultiplezones.
BalancedControls.
Toincreaseflexibilityandtheabilitytorecoverfromasuccessfulattack,themodelemphasizestheneedforabalanceofdetectiveandcorrectivecontrolsinadditiontopreventativecontrolssuchasfirewalls.
Thisincludesafocusonbusinessintelligenceanalyticaltoolstodetectanomalouspatternsthatmayindicateattemptstocompromisetheenvironment.
UserandDataPerimeters.
Recognizingthatprotectingtheenterprisenetworkboundaryisnolongeradequate,weneedtotreatusersanddataasadditionalsecurityperimetersandprotectthemaccordingly.
Thismeansanincreasedfocusonuserawarenessaswellasdataprotectionbuiltintotheinformationassets.
I'lldescribeeachofthefourcornerstonesinmoredetail.
TrustCalculationThetrustcalculationplaysanessentialroleinprovidingtheflexibilityrequiredtosupportarapidlyexpandingnumberofdevicesandusagemodels.
Thecalculationenablesustodynamicallyadjustusers'levelsofaccess,dependingonfactorssuchasthedevicesandnetworkstheyarecurrentlyusing.
Itcalculatestrustintheinteractionbetweenthepersonordevicerequestingaccess(source)andtheinformationrequested(destination).
Thecalculationconsistsofasourcescoreandadestinationscore,takingintoaccountthecontrolsavailabletomitigaterisk.
AsshowninFigure7-1,theresultofthiscalculationdetermineswhethertheuserisallowedaccessandthetypeofaccessprovided.
Chapter7ANewSecurityArchitecturetoImproveBusinessAgility93Figure7-1.
Trustcalculation.
Source:IntelCorporation,2012SourceScoreTrustinthesource,orrequestor,iscalculatedbasedonthefollowingfactors:Who.
Theidentityoftheuserorservicerequestingaccessandourconfidencelevelintheauthenticationmechanismused—howconfidentarewethatusersarewhotheysaytheyareWhat.
Thedevicetype,itscontrolcapabilities,ourabilitytovalidatethosecontrols,andtheextenttowhichIntelITmanagesthedevice.
Where.
Theuser'sorservice'slocation.
Forexample,auserwhoisinsidetheIntelenterprisenetworkismoretrustedthanthesameuserconnectingthroughapublicnetwork.
Theremayalsobeotherconsiderations,suchasthegeographicalregionwheretheuserislocated.
Chapter7ANewSecurityArchitecturetoImproveBusinessAgility94DestinationScoreThisiscalculatedbasedonthesamethreefactors,buttheseareconsideredfromtheperspectiveofthedestination—theinformationthesourceistryingtoaccess:Who.
Theapplicationthatstorestherequesteddata.
Someapplicationscanenforcegreatercontrols,suchasenterpriserightsmanagement(ERM),andthereforeprovideahigherleveloftrust.
What.
Thesensitivityoftheinformationbeingrequestedandotherconsiderations,suchasourabilitytorecoveritifcompromiseoccurs.
Where.
Thesecurityzoneinwhichthedataresides.
AvailableControlsThetrustcalculationalsotakesintoaccountthesecuritycontrolsavailableforthezone.
Iftheonlycontrolsavailablearecontrolsthatsimplyblockorallowaccess,wemightdenyaccessduetolackofotheroptions.
However,ifwehaveextensivepreventativecontrolswithhighlygranularlevelsofaccess,detailedlogs,andhighlytunedsecuritymonitoring—aswellastheabilitytorecoverfromorcorrectproblems—thenwecanallowaccesswithoutcreatingadditionalrisk.
CalculatingTrustThetrustcalculationaddsthesourcescoreandthedestinationscoretoarriveataninitialtrustlevel.
Theavailablecontrolsarethenconsideredtomakeafinaldecisionaboutwhetheraccessisallowedand,ifso,how.
Thiscalculationisperformedbyalogicalentitycalledapolicydecisionpoint(PDP),whichispartoftheauthenticationinfrastructureandmakesaccesscontroldecisionsbasedonasetofpolicies.
Basedontheresultsofthiscalculation,thePDPmakesadecision,allocatingatrustlevelthatdetermineswhethertheusercanaccesstherequestedresourceandthetypeofaccessthatisallowed.
Broadly,thedecisionwillfallintooneofthefollowingcategories:AllowaccessDenyaccessAllowaccesswithlimitationsormitigationThistrustcalculationthereforeallowsustodynamicallyapplygranularcontroloveraccesstospecificresources.
Forexample,employeesusingIT-manageddeviceswithadditionalhardwarefeaturessuchasatrustedplatformmodule(TPM),globalpositioningsystem(GPS),andfulldiskencryptionwouldbeallowedaccesstomoreresourcesthanwhenusingdevicesthatlackthosefeatures.
EmployeesdirectlyconnectedtotheIntelnetworktypicallygetgreateraccessthanwhenusingapublicnetwork.
Ifweareunabletoverifythelocationofahigh-securitydevicesuchasamanagedPC,wewouldallowlessaccess.
Chapter7ANewSecurityArchitecturetoImproveBusinessAgility95Thetrustcalculationalsocanbeusedformorefine-graineddistinctionsbetweendifferentdevicemodels.
Forexample,wecouldprovidedifferentlevelsofaccessbasedonsmartphonemanageability,hardware-enabledauthenticationandencryption,andinstalledapplications.
Weanticipatesituationsinwhichthetrustlevelisnotadequatetoallowanyaccess,butthereisstillabusinessrequirementtoallowaconnectionortransactiontooccur.
Intheseconditions,theresultofthetrustcalculationcouldbeadecisiontoallowaccesswithlimitationsorwithcompensatingcontrolsthatmitigatetherisk.
Forexample,ausermightbeallowedread-onlyaccessormightbepermittedaccessonlyifadditionalmonitoringcontrolsareinplace.
We'reimplementingthistrustcalculationacrossIntel'senvironment.
Today,thetrustcalculationmakesdecisionsbasedoninformationgatheredfromcomponentsatmultiplelevelsoftheinfrastructure,suchasnetworkgateways,accesspoints,anduserdevices.
Oncethetrustcalculationmechanismisinplace,wecanextendittoincludeinformationfromabroaderrangeofsources.
Forexample,thecalculationmighttakeintoaccountthelevelofhardware-enforcedsecurityfeaturesbuiltintotheuser'sdevice.
Thiswouldallowustoprovidegreateraccesstouserswhohavemore-trusteddevices.
Thetrustcalculationcanbeusedtodetermineaccesstointernalsystemsbybusinesspartnersaswellasemployees.
Let'ssaywe'recollaboratingwithanothercompanyonthedesignofanewproduct.
Anengineeratthatcompanywantsaccesstoaspecificdocument.
Wecanaddavarietyofcriteriatothetrustcalculationfordecidingwhethertograntaccess.
Didtheengineer'srequestoriginatewithinthebusinesspartner'senterprisenetworkIsitconsistentwiththetypeofrequestthatwe'dexpectfromanengineerIfso,wehaveahigherleveloftrustintherequestor.
Ifwecannotestablishanadequateleveloftrustintheuser'sdevice,butotherfactorsprovideenoughconfidencetograntaccess,wemightprovideone-timeaccessforaspecificjob.
Wecoulddothisbyallowingadocumenttobedownloaded,butonlywithinacontainerthatensuresthedocumentiscompletelyremovedfromtheuser'sdeviceoncethejobiscompleted.
Longerterm,thetrustcalculationcouldbecomeamechanismthatisusedtodetermineaccesstobothinternalandexternalresources.
IntelIT,likemanycompanies,isusingsomeexternalcloud-basedapplications,whiledevelopinganinternalprivatecloudformostapplications.
Inthefuture,weanticipategreateruseofahybrid-cloudapproach.
Thetrustcalculationcouldbeusedtomanageidentityandaccessforboth.
SecurityZonesThearchitecturedividestheITenvironmentintomultiplesecurityzones.
Theserangefromuntrustedzonesthatprovideaccesstolessvaluabledataandlessimportantsystemstotrustedzonescontainingcriticaldataandresources.
Becausethehigher-trustzonescontainmorevaluableassets,theyareprotectedwithagreaterdepthandrangeofcontrols,andwerestrictaccesstofewertypesofdevicesandapplications,asshowninFigure7-2.
However,devicesallowedaccesstohigher-trustzonesalsohavemorepower—theymaybeabletoperformactionsthatarenotallowedwithinlower-trustzones,suchascreatingormodifyingenterprisedata.
Chapter7ANewSecurityArchitecturetoImproveBusinessAgility96Aligningtheinfrastructureinthisfashionprovidesanexcellentwaytoright-sizesecuritycontrolssothatsecurityresourcesareutilizedeffectively.
Italsohelpsimprovetheuserexperiencebyenablingemployeestochoosefromawiderrangeofdevices,suchassmartphones,forlower-riskactivities.
Accesstozonesisdeterminedbytheresultsofthetrustcalculationandiscontrolledbypolicyenforcementpoints(PEPs).
PEPsmayincludearangeofcontrols,includingfirewalls,applicationproxies,intrusiondetectionandpreventionsystems,authenticationsystems,andloggingsystems.
Communicationbetweenzonesistightlyrestricted,monitored,andcontrolled.
WeseparatezonesbylocatingthemondifferentphysicalorvirtualLANs;PEPscontrolcommunicationbetweenzones.
Thismeansthatifonezoneiscompromised,wecanpreventtheproblemfromspreadingtootherzonesorincreaseourchancesofdetectionifitdoesspread.
Inaddition,wecanusePEPcontrols,suchasapplicationproxies,toprovidedevicesandapplicationsinlower-trustzoneswithlimited,controlledaccesstospecificresourcesinhigher-trustzoneswhenrequired.
Thearchitectureincludesthreeprimarycategoriesofsecurityzone:untrusted,selective,andtrusted.
Withinthezones,therearemultiplesubzones.
UntrustedZonesThesezoneshostdataandservices(ortheinterfacestothem)thatcanbeexposedtountrustedentities.
Thisallowsustoprovidewidespreadaccesstoalimitedsetofresourcesfromnon-managedconsumerdevices,withoutincreasingtherisktohigher-valueresourceslocatedinotherzones.
Untrustedzonesmightprovideaccesstoenterpriseresources,suchascorporatee-mailandcalendars,ortheymightsimplyprovideInternetaccess.
Figure7-2.
Asthevalueofanassetincreases,thedepthandspanofcontrolsincrease,whilethenumberofalloweddevices,applications,andlocationsdecrease.
Source:IntelCorporation,2012Chapter7ANewSecurityArchitecturetoImproveBusinessAgility97Thesezonesareregardedas"sharktanks,"withahighriskofattackandcompromise.
Therefore,detectiveandcorrectivecontrolsareneededtomitigatethisrisk.
Thesecontrolsmightincludeahighlevelofmonitoringtodetectsuspectactivityandcorrectioncapabilitiessuchasdynamicremovalofuserprivilege.
Weanticipateaneedtoprovidecontrolledaccessfromthesezonestoresourcesinhigher-trustzones.
Forexample,anemployeeusinganuntrusteddevicemightbeallowedlimited,read-onlyaccesstocustomerdatalocatedinatrustedzone;ortheirdevicemightneedaccesstoadirectoryserverinatrustedzonetosende-mail.
Weexpecttoprovidethiscontrolledaccessusingapplicationproxies.
Theseproxiesactassecureintermediaries—evaluatingtherequestfromthedevice,gatheringtheinformationfromtheresourceinatrustedzone,andpassingittothedevice.
SelectiveZonesSelectivezonesprovidemoreprotectionthanuntrustedzones.
Examplesofservicesinthesezonesincludeapplicationsanddataaccessedbycontractors,businesspartners,andemployees,usingclientdevicesthataremanagedorotherwiseprovidealeveloftrust.
Selectivezonesdonotcontaincriticaldataorhigh-valueIntelintellectualproperty.
Severalselectivesubzonesprovideaccesstodifferentservicesorusers.
TrustedZonesTrustedzoneshostcriticalservices,data,andinfrastructure.
Theyarehighlysecuredandlockeddown.
Examplesofserviceswithinthesezonesareadministrativeaccesstodatacenterserversandnetworkinfrastructure,factorynetworksanddevices,enterpriseresourceplanning(ERP)applications,anddesignengineeringsystemscontainingintellectualproperty.
Accordingly,wemightonlyallowdirectaccesstotheseresourcesfromtrustedsystemslocatedwithintheenterprisenetwork,andallaccesswouldbemonitoredcloselytodetectanomalousbehavior.
AtIntel,wehaveimplementedsecurehigh-trustzonesaspartofourtransitiontoanenterpriseprivatecloud.
Implementingthesezoneswasakeystepinallowingustomoveseveralcategoriesofapplicationontovirtualizedcloudinfrastructure,includinginternalapplicationsrequiringhighsecurity,aswellasexternallyfacingapplicationsusedtocommunicatewithbusinesspartners.
Thesecurityfeaturesinthesetrustedzonesincludeapplicationhardeningandincreasedmonitoring.
Wecontinuetoaddfurthersecuritycapabilitiesovertime.
NEWSECURITYARCHITECTUREINACTION:ADAYINTHELIFEOFANEMPLOYEEThisexample(illustratedinFigure7-3)describeshowthenewsecurityarchitectureenablestheIntelsalesforcetoaccesstheinformationtheyneedinthecourseofaday.
Atthesametime,thearchitectureprotectsIntel'ssecuritybydynamicallyadjustingthelevelofaccessprovided,basedontheuser'sdeviceandlocation,andbymonitoringforanomalousbehavior.
Chapter7ANewSecurityArchitecturetoImproveBusinessAgility98Theemployeetravelstoacustomersite.
Theemployeeisusingapersonalsmartphonewithlimitedsecurityfeaturesandsoisallowedaccessonlytoservicesinuntrustedzones.
Fromhere,theemployeecanviewlimitedcustomerinformation,includingrecentorders,extractedfromanenterpriseresourceplanning(ERP)systeminatrustedzone—butonlythroughanapplicationproxyserver,whichprotectsthetrustedzonebyactingasanintermediary,evaluatinginformationrequests,accessingtheERPsystem,andrelayingtheinformationtotheuser.
Ifasmartphonerequestsanabnormallylargenumberofcustomerrecords—anindicationthatitmayhavebeenstolen—furtheraccessfromthesmartphoneisblocked.
Tohelpunderstandthereasonfortheanomalousaccess,thereisincreasedmonitoringoftheemployee'sattemptstoaccessthesystemfromanydevice.
Theemployeereachesthecustomersiteandlogsintotheenterprisenetworkfromacompany-ownedmobilebusinessPC.
Becausethisdeviceismoretrusted,theemployeenowhasaccesstoadditionalcapabilitiesavailableinselectivezones,suchastheabilitytoviewpricingandcreateordersthatarerelayedbyanapplicationproxytotheERPsysteminatrustedzone.
Figure7-3.
Thenewsecurityarchitecturedynamicallyadjuststheuser'saccesstoinformation,basedonfactorssuchastheuser'sdeviceandlocation.
Source:IntelCorporation,2012Chapter7ANewSecurityArchitecturetoImproveBusinessAgility99Theemployeereturnstothecompany'sofficeandconnectstothecorporatenetwork.
NowtheemployeeisusingatrusteddevicefromatrustedlocationandhasdirectaccesstotheERPsysteminatrustedzone.
BalancedControlsOverthepastdecade,enterprisesecurityhasfocusedheavilyonpreventativecontrolssuchasfirewallsandintrusionpreventionsystems.
Thisapproachoffersclearbenefits:itislessexpensivetopreventanattackthantocorrectproblemsafteronehasoccurred,anditiseasytoseewhenfirewallshavesuccessfullypreventedanattemptedcompromise.
However,thenewsecuritymodelrequiresthatwebalancepreventativecontrolswithdetective(monitoring)andcorrectivecontrols,forseveralreasons.
First,thefocusofthenewmodelisonenablingandcontrollingaccessfromawiderrangeofusersanddevices,ratherthanonpreventingaccess.
Second,thecontinuallychangingthreatlandscapemakesitnecessarytoassumethatcompromisewilloccur;allpreventativecontrolswilleventuallyfail.
Onceattackershavegainedaccesstotheenvironment,thepreventativecontrolstheyhavebypassedareworthless.
Byincreasingtheuseofdetectivecontrolsandimplementingmoreaggressivecorrectivecontrols,wecanmitigatetheriskofallowingbroaderaccess.
Thesecontrolsalsoincreaseourabilitytosurviveandrecoverfromasuccessfulattack.
USINGSECURITYBUSINESSINTELLIGENCETODETECTSUSPICIOUSBEHAVIORLikeanylargeorganization,Intelhasexperiencedsecurityissuesinvolvingbothexternalattackersandinsiders,includingattemptstostealintellectualproperty.
Aswe'veinvestigated,wehaveidentifiedmarkersandindicatorsthatarefrequentlyassociatedwiththeseevents.
Werealizedthatifwehadbeenabletospottheseindicatorssooner,wecouldhaverespondedandmitigatedthethreatsmorequickly.
Securitybusinessintelligenceisakeytechnologythatwecanusetodetectsuspiciousbehaviorastheenvironmentbecomesmorecomplexandattackersbecomemoreadeptatconcealingcompromises.
Analyticaltoolsautomatetheprocessofanalyzinglargevolumesofdatatodetectandmonitoranomalousactivity,allowingustodetectproblemsthatwemightotherwisemiss.
Thesecapabilitiesaresimilartothosealreadyimplementedbyfinancialinstitutionstopreventfraudulentcredit-cardtransactions,andbyonlineconsumerservicestopreventtheftofuserdata.
Banksmonitoraccessattemptsandonlinetransactionstodeterminewhethertotrusttheuser'sidentityandwhethertoallowtheuser'sactivity.
Iftheuseristryingtotransferalargesumtoanexternalaccount,thebank'ssystemsmaycomparethetransactionwiththeuser'spreviousbehaviortoseeifitappearstobeabnormal.
Tomitigaterisk,thebankmaydelaylargetransferssoitcanperformadditionalanalysisandinformtheaccountownerbye-mail.
Chapter7ANewSecurityArchitecturetoImproveBusinessAgility100Inasimilarway,wecanusesecuritybusinessintelligence—analysisandcorrelationofdatagatheredbymonitoring—toanalyzepatternsofbehavior.
Thiscandetectandthwartpossibleattacks.
Onalargescale,loggingdatageneratedbyserversandsensorsacrossthenetworkcanbecollectedintoadatabaseforanalysis.
AtIntel,weareusinganalytictoolstocorrelatethisaggregateddataandflaganomaliesforfurtherinvestigation.
Forexample,iftrafficwithinaserverclusterbecomesabnormallyhigh,itmightindicatethatabotnetisexploitingoneoftheserverstobroadcasttrafficacrosstheWeb.
Securitybusinessintelligencecanalsobeappliedatthelevelofindividualusersanddevices.
AtIntel,we'reimplementingmonitoringtechnologythattracksusers'loginsandaccessattempts,asIdescribedinChapter5.
Ourstrategyistomakelogininformationavailabletouserssothattheycanhelptospotunauthorizedaccessattempts.
Inthefuture,Ienvisagethatthesystemcouldanalyzeusers'historicalbehaviorpatternstodeterminehowtorespondwhenusersrequestaccesstoresources.
Thesystemcouldcomparetherequestwiththeuser'spreviousactions:whathaveyoudonebefore,andisthisrequestconsistentwiththosebehaviorsorisitananomalyandthereforesuspiciousIftherequestappearsconsistentwithpreviousbehavior,thesystemwouldpasstherequesttothetrustcalculation;ifitappearsanomalous,thesystemmightdenytherequestandalertthesecurityteam.
WithinIntel,wehavealsodeployedadashboardthatprovidesgranularinformationaboutinfectedclientsandservers,boostingourabilitytointervenequicklyandaccurately.
Duetooureffortstodetectandremovemalwarebeforeinfectionsoccur,weachieveda33percentreductioninmalwareimpactsin2011,despiteexperiencinga50percentincreaseinthenumberofvariants(Intel2012a).
Wealsoplantoaddapredictiveenginethatenablesproactiveprotectionandsimulationsthatcanimproveourabilitytorespondtothreats.
Thebalancebetweenpreventative,detective,andcorrectivecontrolswillvary,dependingonthesecurityzone.
Inhigh-trustzones,weimplementextensivemonitoringtodetectpossibleattemptstostealdataorcompromisecriticalsystems.
Redundancywithineachtypeofcontrolcanbeusedtoprovideadditionalprotection.
Thefollowingincludespossibleexamplesofusingdetectiveandpreventativecontrols:AnIntelemployeeattemptstosendaconfidentialdocumenttoanon-Intele-mailaddress.
Monitoringsoftwaredetectstheattempt,preventsthedocumentfrombeingsentoutsidethefirewall,andaskstheIntelemployeeifheorshereallyintendedtodothis.
Iftheemployeeconfirmsthatthiswasintended,thedocumentmaybetransmitted—orifthedocumentishighlysensitive,aredactedversionmaybesent.
Chapter7ANewSecurityArchitecturetoImproveBusinessAgility101Inappropriateuseofadocumentprotectedwithenterpriserightsmanagementtechnologyresultsinrevocationofaccesstothedocument.
Thesystemallowsaccesstospecificdocumentsbuttrackstheactivity.
Ausercandownloadafewdocumentswithoutcausingconcerns.
However,iftheuserattemptstodownloadhundredsofdocuments,thesystemslowsdownthespeedofdelivery(forinstance,onlyallowingtentobecheckedoutatatime)andalertstheuser'smanager.
Ifthemanagerapproves,theuserisgivenfasteraccess.
Thedetectionofaninfectedsystemplacesthesystemonaremediationnetwork,isolatingthesystemandrestrictingaccesstoenterpriseinformationandapplications.
Thesystemmayretainsomeabilitytoaccesscorporateassets,butallactivityiscloselyloggedtoenableincidentresponseifnecessary.
Whenasystemisfoundtobecompromised,weexamineallitsrecentactivitiesandinteractionswithothersystems.
Additionalmonitoringofthosesystemsisautomaticallyenabled.
UsersandData:TheNewPerimetersTheconceptofbalancedcontrolsalsoextendstotheprotectionofusersanddata.
Traditionalnetworksecurityboundariesaredissolvingwiththeproliferationofnewdevicesandusers'expectationsthattheyshouldbeabletoaccessinformationfromanywhereatanytime.
Usersareunderdirectassaultfromabarrageofattacksdesignedtotrickthemintotakingactionsthatcancompromisetheinformationontheirdevicesoronenterprisesystems.
Thesetrendsmeanthatweneedtothinkmorebroadlyabouthowweprotectinformation,aswellastheusersofthisinformation.
Whilewecontinuetoimplemententerprisenetworkcontrols,suchasperimeterdefensesandthedetectivecontrolsdescribedearlier,weneedtosupplementthesecontrolswithafocusontheusersandontheprimaryassetswearetryingtoprotectsuchasintellectualproperty.
Thenewarchitecturethereforeexpandsourdefensestotwoadditionalperimeters:thedataitselfandtheuserswhohaveaccesstothedata.
DataPerimeterImportantdatashouldbeprotectedatalltimes—whenitiscreated,stored,andtransmitted.
Thisbecomesincreasinglychallengingaswemovedatatomoreandmoredevicesandletmorepeopleaccessit.
Howdoweprotectinformationwhenit'slocatedoutsidethephysicalperimeteronapersonaldeviceAtIntelIT,we'reimplementingtechnologiesthatcloselyintegrateprotectionwithhigh-valuedatasothatthedataremainsprotectedasitmovestodifferentdevicesandlocations.
Technologies,suchasenterpriserightsmanagementanddataleakprevention,canbeusedtowatermarkandtaginformationsothatwecantrackandmanageitsuse.
Withenterpriserightsmanagement,thecreatorofadocumentcandefineexactlywhoChapter7ANewSecurityArchitecturetoImproveBusinessAgility102hasaccessrightsthroughoutthelifeofthedocumentandcanrevokeaccessatanypoint.
Datalosspreventionisusedtotagdocuments,tracktheirmovements,andpreventtransferoutsidetheorganizationifnecessary.
UserPerimeterAsIdescribedinChapter5,peoplearepartofthesecurityperimeter,andweneedtotreatthemassuch.
Userscanbecomesecurityrisksforavarietyofreasons.
Theyaretargetedmorefrequentlyinsocialengineeringattacks,andtheyaremorevulnerabletotheseattacksbecausetheirpersonalinformationisoftenreadilyavailableonsocialnetworkingsites.
Theymayalsoclickmaliciouslinksine-mail,downloadmalware,orstoredataonportabledevicesthatthenarelost.
AtIntel,we'vefoundthatacombinationoftraining,incentives,andotheractivitiescanhelpinstillinformationsecurityandprivacyprotectionintothecorporatecultureandsuccessfullyencouragesemployeestoownresponsibilityforprotectingenterpriseandpersonalinformation.
We'veseenoureffortspayoff,withemployeescallingthehelpdeskorsendinge-mailalertswhentheynoticesomethingthatdoesn'tseemright.
Asdiscussedinthesidebar("UsingSecurityBusinessIntelligencetoDetectSuspiciousBehavior"),ourstrategyalsoincludesmakingaccountaccesslogsavailabletouserssothattheycanhelpspotunauthorizedaccessattempts.
ConclusionThischapterdescribesanewarchitecturedesignedtosupporttheProtecttoEnablemission.
Itsgoalistoallowfasteradoptionofnewservicesandcapabilitieswhileimprovingsurvivability.
AtIntel,webelievethatthisarchitecturecanbeusedtomeetabroadrangeofevolvingrequirements,includingnewusagemodelsandthreats.
Becauseofthis,weareworkingtoingrainthismodelintoallaspectsofIntelIT,fromdevelopmenttooperations.
We'vealreadyusedaspectsofthearchitecturetoprovidesolutionstochallengingusecases,whileactuallyreducingrisk.
Forexample,we'vebeenabletomoveimportantinternalandInternet-facingapplicationstoaprivatecloudbyutilizinghigh-trustzones.
We'vesuccessfullyusedvariousapproachestoprotecttheuseranddataperimeters.
Wealsousedbalancedcontrolsandtrustzonestoenablenetworkaccessfromemployee-owneddevices.
Insomecases,projectshaveseentheirsecurityoverheaddecreasebyadoptingthismodel.
Ibelievethatthearchitecturecouldprovidesimilarvaluetootherorganizationsfacingsimilarchallenges.
Bypublishinginformationaboutthearchitecture,wehopetoencourageotherstotakeadvantageofthisarchitecturewhereveritmeetstheirneeds.
Wealsohopethatmakingthisinformationavailablewillstimulatemorediscussionandideas,andthatotherswillbuildontheseconceptstocreatefurtherinnovationsthatbenefitallofus.
—JackWelchSomeStarTrekepisodesfeaturesuspense-filledbattlesinwhichadversariesusesophisticatedphase-shiftingweaponsthatcanberapidlyadjusteduntiltheyfindawaytopenetratestaticforce-fielddefenses.
Forabeleagueredstarship,theonlyeffectiveresponseistousesimilarlyadaptableandfast-changingshields.
Asinformationsecurityprofessionals,wealsoneedextremelyagiledefensesthatcanbequicklyadaptedtomeetnewdemands.
Attackersarecontinuallyadapting,anddefendersalsoneedtocontinuallyadapt.
Butrapidlyevolvingthreatsareonlypartofthechallenge.
ThetechnologylandscapeischangingjustasfastduetotrendslikeITconsumerization.
AsIntel'sinformationriskandsecuritygroupconsidersthefuture,werealizethatweneedtoradicallychangeourapproachinordertofacethechallengesaheadandsupporttheProtecttoEnablemission.
Weneedamoreagilesecurityarchitecturethatcanquicklylearnandadapttonewchallengesastheyemerge.
Becausetheenvironmentischangingsoquickly,inwayswecannotcontrol,it'simpossibletopredictallthefuturechallengeswe'llneedtoface.
Weneedanarchitecturethatcanlearntomanagewhatwedon'tknow.
Thisflexibilitywillhelpthebusinessmovemorequickly,byenablingustorapidlyadoptnewtechnologiesandemergingusagemodelswhilecontinuingtoprovidesecurityintheever-evolvingthreatlandscape.
Alearningsystemishardertodefeatbecauseitcanmorequicklyadaptinresponsetonewattacks.
Afterintensebrainstormingsessions,ourinformationriskandsecurityteamdevisedanewsecurityarchitecture.
ThisarchitectureisourimplementationoftheProtecttoEnablestrategy.
Inthischapter,I'llprovideahigh-leveloverviewofthearchitectureanddescribehowitmeetssomekeysecuritychallenges.
ThoughtheoverviewisbasedonourworkatIntel,IbelievethatthisisanovelapproachtoenterprisesecuritythatmaybevaluableChapter7ANewSecurityArchitecturetoImproveBusinessAgility88tomanyotherorganizationsfacingtheseuniversalchallenges.
Myconversationswithpeersatothercompanieshavevalidatedthisview.
Manyofthemareconsideringsimilarstrategiesandinsomecaseshavebegunimplementingthem.
WeareimplementingthisarchitectureacrossIntel'sITenvironmentinaradicalfive-yearredesignofourinformationsecuritytechnology.
Evenwhiletheimplementationisinprogress,thenewarchitecturehasalreadydeliveredresultsbyhelpingusprovideinnovativesolutionstochallengingusecaseswhileactuallyreducingrisk.
IntelIThaspublishedmoredetaileddescriptionscoveringseveralaspectsofthearchitecture(Ben-Shalometal.
2011,SunderlandandChandramouly2011,Gutierrezetal.
2012),andweexpecttocontinuetopublishinformationinthefuture.
Akeyaspectofthearchitectureisthatitprovidesmoreflexible,dynamic,andgranularsecuritycontrolsthantraditionalenterprisesecuritymodels.
Thishelpsusaccommodateusagemodelssuchasbring-your-own-device(BYOD).
Wecanprovideuserswithdifferentlevelsofaccessdependingonfactorssuchasthedevicestheyareusingandtheirlocation.
Toachievethis,thetechnologydynamicallyadjustsauser'saccessprivilegesasthelevelofriskchanges.
Forexample,anemployeeshouldhavemorelimitedaccesstooursystemswhenusingaless-securedevicethanwhenusingahardened,fullymanagedenterprise-classsystem.
Thenewarchitecturegreatlyimprovesthreatmanagement.
Asnewrisksappear,weneedtobeabletoquicklyrecognizewhichoneswecanmitigate,learnasmuchaswecan,andtakeactionasquicklyaspossible.
AtIntel,weusemanyinformationsourcestogainanunderstandingoftherisks.
Collectively,thesesourcesprovideacontinuousfeedofcollectiveintelligencethatwecanusetolearn,adapt,andevolve.
AsIdescribedinChapter6,weuseemergingthreatanalysistohelpusanticipatefuturerisks.
Butourarchitecturealsoassumesthatcompromiseisinevitableandfocusesheavilyonsurvivability.
Weareapplyingsecuritymonitoringandbusinessintelligencetoanalyzepatternsofbehavioranddetectanomaliesthataresymptomsofattacks.
Withthisknowledge,wecanfurtherinvestigateandapplymitigationwherenecessary.
Inthefuture,thisapproachcouldbeextendedbyautomaticallytakingcorrectiveactionwhereitmakessensetodoso.
BusinessTrendsandArchitectureRequirementsBeforedivingintothespecificsofthearchitecture,I'llrecapsomeofthekeybusinessandtechnologytrends,focusingonhowtheydrivetheneedforspecificcapabilitiesinsecuritytechnology.
ITConsumerizationAsIdiscussedinChapter5,consumerizationisamajorITthemewithever-broadeningimpact.
Itincludesseveraltrends,includingtheadoptionofnewapplicationsandsupportforconsumerdevices.
ManyofIntel'shighlymobileemployeeswanttousetheirownconsumerdevices,suchassmartphonesandtablets,forwork.
Thisincreasesproductivitybyenablingemployeestocollaborateandaccessinformationfromanywhere,atanytime.
TosupportChapter7ANewSecurityArchitecturetoImproveBusinessAgility89this,weprovideaccesstocorporatee-mailandotherapplicationsfromemployee-ownedsmartphonesandtablets.
Somepeoplebelievethatinthefuture,alldeviceswillbeconsumer-owned,andthatenterpriseswillnolongerpurchasedevicesfortheirusers.
Ibelievethismightbethecaseinsomeworkenvironments,butIdoubtthatitwillsuitallorganizations.
Foracompanyprovidingcallcenterservices,withmostemployeesworkingfromhome,itmightmakesensethatemployeesexclusivelyusetheirownpersonalsystemsforwork.
Butthisstrategywouldbemoreriskyforafinancialservicescompanywhoseemployeeshandlehighlysensitiveinformationthat'ssubjecttoextensiveregulatoryrequirements.
Nevertheless,theconsumerizationtrendcontinuestogrowatIntelandotherorganizations.
Accordingly,we'llneedtoprovideemployeeswithalevelofaccesstoIntelresourcesfromanexpandingcontinuumofclientdevices,someofwhichhavemuchweakersecuritycontrolsthantoday'senterpriseclients(seesidebar).
CONSUMERIZINGENTERPRISEITAND"ENTERPRISING"THECONSUMERDiscussionsofITconsumerizationtendtodrawaclearlinebetweenbusinessdevicesthatcanbemanagedandtrusted,andpersonalconsumerdevicesthatareessentiallyunmanagedanduntrusted.
However,notallconsumerdevicesarecreatedequal.
Fromasecuritystandpoint,itmaybemorevaluabletothinkaboutadevice'scapabilitiesthantocategorizeitbasedsolelyonwhetherit'smarketedasanenterprisedeviceorapersonaldevice.
Thesecurityofadevicedependsontheinherentfeaturesofthehardware,operatingsystem,andapplications,andonwhetheritenablesustoaddfurthersecurityandmanageabilitycapabilitiesthatmitigatetherisksofenterpriseuse.
Asthevarietyofconsumerdevices,suchassmartphones,continuestoexpand,usersmaychoosefromdozensofmodelswithdifferentlevelsofsecuritycapabilities.
GreatersecurityandmanageabilitymeansthatITcanplacegreatertrustinthedeviceandprovideacorrespondinglygreaterlevelofaccesstoenterpriseresources.
Extendingthisideafurther,theinformationsecuritygroupcouldevaluatethesecurityofavailableconsumerdevicesandprovideguidanceaboutthelevelofenterpriseaccessthatuserswillbeallowedwitheachdevice.
Usersmayprefertobuyamoresecuredevicebecauseitwillprovidethemmoreaccess.
Withgreateraccess,theycanusethedeviceformoreoftheirdailyworkactivities.
Thisabilityinturnenablesthemtobemoreproductive.
Atthesametime,employeesincreasinglyexpecttohaveavailabletothematworkthetypesofconsumerservicesandcloudapplicationsthattheyuseintheirpersonallives.
Theseincludesocialcomputingapplicationssuchasblogsandwikis,video-sharingsites,andfile-sharingservices.
Chapter7ANewSecurityArchitecturetoImproveBusinessAgility90Weneedasecurityarchitecturethatenablesustomorequicklysupportnewdevicesandprovideaccesstoagreaterrangeofapplicationsanddata,withoutincreasingrisk.
Weneedtobeabletodynamicallyadjustthelevelsofaccessweprovideandthemonitoringweperform,dependingonthesecuritycontrolsoftheclientdevice.
NewBusinessNeedsNearlyallcompaniesnowrelyonagrowingnetworkofbusinesspartners,andconductmanyoftheirinteractionswiththosepartnersonline.
Intelisnoexception—wearedevelopinganincreasingnumberofsystemsforonlinecollaborationwithbusinesspartners.
Also,likemanycompanies,Intelisexpandingintonewmarketsthroughbothorganicgrowthandacquisitions.
Becauseofthesebusinesstrends,mostorganizationsneedtoprovideaccesstoabroaderrangeofusers,manyofwhomarenotemployees.
Manyalsoneedtobeabletosmoothlyintegrateacquiredcompaniesandprovidethemwithaccesstoresources.
Ingeneral,weneedtoquicklyprovidenewusersaccesswhileminimizingriskandprovidingselective,controlledaccessonlytotheresourcestheyneed.
CloudComputingMostorganizationsarealreadyusingcloudservicesinsomeformtoachievebenefitssuchasgreateragilityandlowercost.
Likemanycompanies,IntelITisimplementingaprivatecloudbasedonvirtualizedinfrastructure,andwearealsousingexternalcloudservicesfornoncriticalapplications.
Inthefuture,weexpectgreateruseofhybridcloudsthatusebothinternalandexternalresources.
ThistrendmeansthatITservicesatmanyorganizationswillbeprovidedbyamixtureoftraditionalandcloud-basedinternalandexternalservices.
Duringatypicalday,employeesmayaccessavarietyofdifferentservices,someofwhichareinternalandsomeexternal.
Ultimately,theyshouldbeabletoeasilymovebetweentheseserviceswithoutneedingtologinmultipletimesorevenknowwheretheservicesarelocated.
Securingaccesstocloud-basedservicespresentschallengesthataren'teasilyaddressedusingconventionalsecuritycontrols.
Incloudenvironments,systemsandtheirdataarevirtualizedandmaymigratedynamicallytodifferentnetworklocations.
Thismakesitdifficulttoeffectivelyrestrictaccessusingtraditionalsecuritycontrolssuchasfirewalls,whichrelyonfixedlocationsofsystemsandamorestaticnatureofthedata.
Weneedmuchmoregranularanddynamiccontrolsthatarelinkedtotheresourcesthemselvesratherthanjusttheirnetworklocation.
ChangingThreatLandscapeThethreatlandscapeisevolvingrapidly.
Increasingly,attackersaretakingastealthyapproach,creatingmalwarethatquietlygainsaccessandattemptstoremainundetectedinordertomaintainaccessovertime.
Asthenumberofthreatsincreasesandnewtypesofmalwareemerge,weneedtoassumethatcompromiseisinevitable.
Chapter7ANewSecurityArchitecturetoImproveBusinessAgility91Traditionalenterprisesecurityarchitectureshavereliedlargelyonpreventativecontrolssuchasfirewallslocatedatthenetworkperimeter.
However,ourprimaryfocushasshiftedtoprovidingcontrolledaccesstoabroaderrangeofusersanddevices,ratherthansimplypreventingaccess.
Inaddition,thecontinuallychangingthreatlandscapemakesitnecessarytoassumethatcompromisewilloccur.
Onceattackershavegainedaccesstotheenvironment,thepreventativecontrolstheyhavebypassedareworthless.
Althoughtheseperimetercontrolswillcontinuetohavesomevalue,weneedtoolsthatincreasetheabilitytosurviveandrecoveronceattackershavegainedaccesstotheenvironment.
PrivacyandRegulatoryRequirementsThegrowingemphasisonprivacyrequirementsandtheincreasinglycomplexregulatoryenvironmenthavemanyimplicationsforthewaywemanageinformation.
Someregulationscreatetheneedformorecontroloverwhereinformationisstoredandrequirespecificlevelsofprotectionandtracking.
Ourarchitecturemustprovidethisassurance,allowingustobuildahigh-securityenvironmentandaccesscontrolsappropriatefortheprotectionofhighlyregulatedinformation.
NewArchitectureTomeettheserapidlychangingrequirements,weneedahighlyflexibleanddynamicarchitecture.
Thearchitectureshouldenableustomorequicklyadoptnewdevices,usemodels,andcapabilities;providesecurityacrossanincreasinglycomplexenvironment;andadapttoachangingthreatlandscape.
AtIntel,weformedateamcharteredwithdesigningthisarchitecturefromscratch,takingafreshapproachtoenterprisesecurity,thendetermininghowtoimplementthisnewarchitectureacrossourexistingITenvironment.
Keygoalsincludehelpingincreaseemployeeproductivitywhilesupportingnewbusinessrequirementsandtechnologytrends,includingITconsumerization,cloudcomputing,andaccessbyabroaderrangeofusers.
Atthesametime,thearchitectureisdesignedtoreduceourattacksurfaceandimprovesurvivability—evenasthethreatlandscapegrowsincomplexityandmaliciousness.
Thearchitecturemovesawayfromthetraditionalenterprisetrustmodel,whichisbinaryandstatic.
Withthistraditionalmodel,auserisingeneraleithergrantedordeniedaccesstoallresources;oncegranted,thelevelofaccessremainsconstant.
Thenewarchitecturereplacesthiswithadynamic,multitieredtrustmodelthatexercisesmorefine-grainedcontroloveridentityandaccesscontrol,includingaccesstospecificresources.
Thismeansthatforanindividualuser,thelevelofaccessprovidedmayvarydynamicallyovertime,dependingonavarietyoffactors—suchaswhethertheuserisaccessingthenetworkfromahighlysecuremanageddeviceoranuntrustedunmanageddevice.
Thearchitecture'sflexibilityallowsustotakeadvantageoftrustthat'sbuiltintodevicesatahardwarelevel,aswellastrustinapplicationsandservices.
Increasingly,deviceswillincludehardware-enforcedsecuritydesignedtoensuretheintegrityoftheapplicationsanddataonthedevice.
ThearchitecturetakesthisintoaccountwhenChapter7ANewSecurityArchitecturetoImproveBusinessAgility92determiningwhethertoallowaccesstospecificresources—amore-trustedplatformcanbeallowedgreateraccessthanaless-trustedone.
Thearchitectureisbasedonfourcornerstones:TrustCalculation.
Thisuniqueelementofthearchitecturehandlesuseridentityandaccessmanagement,dynamicallydeterminingwhetherausershouldbegrantedaccesstospecificresourcesand,ifso,whattypeofaccessshouldbegranted.
Thecalculationisbasedonfactorssuchastheuser'sclientdeviceandlocation,thetypeofresourcesrequested,andthesecuritycontrolsthatareavailable.
SecurityZones.
Theinfrastructureisdividedintomultiplesecurityzonesthatprovidedifferentlevelsofprotection.
Theserangefromtrustednetworkzonescontainingcriticaldata,withtightlycontrolledaccess,tountrustedzonescontainingless-valuabledataandallowingbroaderaccess.
Communicationbetweenzonesiscontrolledandmonitored;thishelpsensureuserscanonlyaccesstheresourcesforwhichtheyhavebeenauthorizedandpreventscompromisesfromspreadingacrossmultiplezones.
BalancedControls.
Toincreaseflexibilityandtheabilitytorecoverfromasuccessfulattack,themodelemphasizestheneedforabalanceofdetectiveandcorrectivecontrolsinadditiontopreventativecontrolssuchasfirewalls.
Thisincludesafocusonbusinessintelligenceanalyticaltoolstodetectanomalouspatternsthatmayindicateattemptstocompromisetheenvironment.
UserandDataPerimeters.
Recognizingthatprotectingtheenterprisenetworkboundaryisnolongeradequate,weneedtotreatusersanddataasadditionalsecurityperimetersandprotectthemaccordingly.
Thismeansanincreasedfocusonuserawarenessaswellasdataprotectionbuiltintotheinformationassets.
I'lldescribeeachofthefourcornerstonesinmoredetail.
TrustCalculationThetrustcalculationplaysanessentialroleinprovidingtheflexibilityrequiredtosupportarapidlyexpandingnumberofdevicesandusagemodels.
Thecalculationenablesustodynamicallyadjustusers'levelsofaccess,dependingonfactorssuchasthedevicesandnetworkstheyarecurrentlyusing.
Itcalculatestrustintheinteractionbetweenthepersonordevicerequestingaccess(source)andtheinformationrequested(destination).
Thecalculationconsistsofasourcescoreandadestinationscore,takingintoaccountthecontrolsavailabletomitigaterisk.
AsshowninFigure7-1,theresultofthiscalculationdetermineswhethertheuserisallowedaccessandthetypeofaccessprovided.
Chapter7ANewSecurityArchitecturetoImproveBusinessAgility93Figure7-1.
Trustcalculation.
Source:IntelCorporation,2012SourceScoreTrustinthesource,orrequestor,iscalculatedbasedonthefollowingfactors:Who.
Theidentityoftheuserorservicerequestingaccessandourconfidencelevelintheauthenticationmechanismused—howconfidentarewethatusersarewhotheysaytheyareWhat.
Thedevicetype,itscontrolcapabilities,ourabilitytovalidatethosecontrols,andtheextenttowhichIntelITmanagesthedevice.
Where.
Theuser'sorservice'slocation.
Forexample,auserwhoisinsidetheIntelenterprisenetworkismoretrustedthanthesameuserconnectingthroughapublicnetwork.
Theremayalsobeotherconsiderations,suchasthegeographicalregionwheretheuserislocated.
Chapter7ANewSecurityArchitecturetoImproveBusinessAgility94DestinationScoreThisiscalculatedbasedonthesamethreefactors,buttheseareconsideredfromtheperspectiveofthedestination—theinformationthesourceistryingtoaccess:Who.
Theapplicationthatstorestherequesteddata.
Someapplicationscanenforcegreatercontrols,suchasenterpriserightsmanagement(ERM),andthereforeprovideahigherleveloftrust.
What.
Thesensitivityoftheinformationbeingrequestedandotherconsiderations,suchasourabilitytorecoveritifcompromiseoccurs.
Where.
Thesecurityzoneinwhichthedataresides.
AvailableControlsThetrustcalculationalsotakesintoaccountthesecuritycontrolsavailableforthezone.
Iftheonlycontrolsavailablearecontrolsthatsimplyblockorallowaccess,wemightdenyaccessduetolackofotheroptions.
However,ifwehaveextensivepreventativecontrolswithhighlygranularlevelsofaccess,detailedlogs,andhighlytunedsecuritymonitoring—aswellastheabilitytorecoverfromorcorrectproblems—thenwecanallowaccesswithoutcreatingadditionalrisk.
CalculatingTrustThetrustcalculationaddsthesourcescoreandthedestinationscoretoarriveataninitialtrustlevel.
Theavailablecontrolsarethenconsideredtomakeafinaldecisionaboutwhetheraccessisallowedand,ifso,how.
Thiscalculationisperformedbyalogicalentitycalledapolicydecisionpoint(PDP),whichispartoftheauthenticationinfrastructureandmakesaccesscontroldecisionsbasedonasetofpolicies.
Basedontheresultsofthiscalculation,thePDPmakesadecision,allocatingatrustlevelthatdetermineswhethertheusercanaccesstherequestedresourceandthetypeofaccessthatisallowed.
Broadly,thedecisionwillfallintooneofthefollowingcategories:AllowaccessDenyaccessAllowaccesswithlimitationsormitigationThistrustcalculationthereforeallowsustodynamicallyapplygranularcontroloveraccesstospecificresources.
Forexample,employeesusingIT-manageddeviceswithadditionalhardwarefeaturessuchasatrustedplatformmodule(TPM),globalpositioningsystem(GPS),andfulldiskencryptionwouldbeallowedaccesstomoreresourcesthanwhenusingdevicesthatlackthosefeatures.
EmployeesdirectlyconnectedtotheIntelnetworktypicallygetgreateraccessthanwhenusingapublicnetwork.
Ifweareunabletoverifythelocationofahigh-securitydevicesuchasamanagedPC,wewouldallowlessaccess.
Chapter7ANewSecurityArchitecturetoImproveBusinessAgility95Thetrustcalculationalsocanbeusedformorefine-graineddistinctionsbetweendifferentdevicemodels.
Forexample,wecouldprovidedifferentlevelsofaccessbasedonsmartphonemanageability,hardware-enabledauthenticationandencryption,andinstalledapplications.
Weanticipatesituationsinwhichthetrustlevelisnotadequatetoallowanyaccess,butthereisstillabusinessrequirementtoallowaconnectionortransactiontooccur.
Intheseconditions,theresultofthetrustcalculationcouldbeadecisiontoallowaccesswithlimitationsorwithcompensatingcontrolsthatmitigatetherisk.
Forexample,ausermightbeallowedread-onlyaccessormightbepermittedaccessonlyifadditionalmonitoringcontrolsareinplace.
We'reimplementingthistrustcalculationacrossIntel'senvironment.
Today,thetrustcalculationmakesdecisionsbasedoninformationgatheredfromcomponentsatmultiplelevelsoftheinfrastructure,suchasnetworkgateways,accesspoints,anduserdevices.
Oncethetrustcalculationmechanismisinplace,wecanextendittoincludeinformationfromabroaderrangeofsources.
Forexample,thecalculationmighttakeintoaccountthelevelofhardware-enforcedsecurityfeaturesbuiltintotheuser'sdevice.
Thiswouldallowustoprovidegreateraccesstouserswhohavemore-trusteddevices.
Thetrustcalculationcanbeusedtodetermineaccesstointernalsystemsbybusinesspartnersaswellasemployees.
Let'ssaywe'recollaboratingwithanothercompanyonthedesignofanewproduct.
Anengineeratthatcompanywantsaccesstoaspecificdocument.
Wecanaddavarietyofcriteriatothetrustcalculationfordecidingwhethertograntaccess.
Didtheengineer'srequestoriginatewithinthebusinesspartner'senterprisenetworkIsitconsistentwiththetypeofrequestthatwe'dexpectfromanengineerIfso,wehaveahigherleveloftrustintherequestor.
Ifwecannotestablishanadequateleveloftrustintheuser'sdevice,butotherfactorsprovideenoughconfidencetograntaccess,wemightprovideone-timeaccessforaspecificjob.
Wecoulddothisbyallowingadocumenttobedownloaded,butonlywithinacontainerthatensuresthedocumentiscompletelyremovedfromtheuser'sdeviceoncethejobiscompleted.
Longerterm,thetrustcalculationcouldbecomeamechanismthatisusedtodetermineaccesstobothinternalandexternalresources.
IntelIT,likemanycompanies,isusingsomeexternalcloud-basedapplications,whiledevelopinganinternalprivatecloudformostapplications.
Inthefuture,weanticipategreateruseofahybrid-cloudapproach.
Thetrustcalculationcouldbeusedtomanageidentityandaccessforboth.
SecurityZonesThearchitecturedividestheITenvironmentintomultiplesecurityzones.
Theserangefromuntrustedzonesthatprovideaccesstolessvaluabledataandlessimportantsystemstotrustedzonescontainingcriticaldataandresources.
Becausethehigher-trustzonescontainmorevaluableassets,theyareprotectedwithagreaterdepthandrangeofcontrols,andwerestrictaccesstofewertypesofdevicesandapplications,asshowninFigure7-2.
However,devicesallowedaccesstohigher-trustzonesalsohavemorepower—theymaybeabletoperformactionsthatarenotallowedwithinlower-trustzones,suchascreatingormodifyingenterprisedata.
Chapter7ANewSecurityArchitecturetoImproveBusinessAgility96Aligningtheinfrastructureinthisfashionprovidesanexcellentwaytoright-sizesecuritycontrolssothatsecurityresourcesareutilizedeffectively.
Italsohelpsimprovetheuserexperiencebyenablingemployeestochoosefromawiderrangeofdevices,suchassmartphones,forlower-riskactivities.
Accesstozonesisdeterminedbytheresultsofthetrustcalculationandiscontrolledbypolicyenforcementpoints(PEPs).
PEPsmayincludearangeofcontrols,includingfirewalls,applicationproxies,intrusiondetectionandpreventionsystems,authenticationsystems,andloggingsystems.
Communicationbetweenzonesistightlyrestricted,monitored,andcontrolled.
WeseparatezonesbylocatingthemondifferentphysicalorvirtualLANs;PEPscontrolcommunicationbetweenzones.
Thismeansthatifonezoneiscompromised,wecanpreventtheproblemfromspreadingtootherzonesorincreaseourchancesofdetectionifitdoesspread.
Inaddition,wecanusePEPcontrols,suchasapplicationproxies,toprovidedevicesandapplicationsinlower-trustzoneswithlimited,controlledaccesstospecificresourcesinhigher-trustzoneswhenrequired.
Thearchitectureincludesthreeprimarycategoriesofsecurityzone:untrusted,selective,andtrusted.
Withinthezones,therearemultiplesubzones.
UntrustedZonesThesezoneshostdataandservices(ortheinterfacestothem)thatcanbeexposedtountrustedentities.
Thisallowsustoprovidewidespreadaccesstoalimitedsetofresourcesfromnon-managedconsumerdevices,withoutincreasingtherisktohigher-valueresourceslocatedinotherzones.
Untrustedzonesmightprovideaccesstoenterpriseresources,suchascorporatee-mailandcalendars,ortheymightsimplyprovideInternetaccess.
Figure7-2.
Asthevalueofanassetincreases,thedepthandspanofcontrolsincrease,whilethenumberofalloweddevices,applications,andlocationsdecrease.
Source:IntelCorporation,2012Chapter7ANewSecurityArchitecturetoImproveBusinessAgility97Thesezonesareregardedas"sharktanks,"withahighriskofattackandcompromise.
Therefore,detectiveandcorrectivecontrolsareneededtomitigatethisrisk.
Thesecontrolsmightincludeahighlevelofmonitoringtodetectsuspectactivityandcorrectioncapabilitiessuchasdynamicremovalofuserprivilege.
Weanticipateaneedtoprovidecontrolledaccessfromthesezonestoresourcesinhigher-trustzones.
Forexample,anemployeeusinganuntrusteddevicemightbeallowedlimited,read-onlyaccesstocustomerdatalocatedinatrustedzone;ortheirdevicemightneedaccesstoadirectoryserverinatrustedzonetosende-mail.
Weexpecttoprovidethiscontrolledaccessusingapplicationproxies.
Theseproxiesactassecureintermediaries—evaluatingtherequestfromthedevice,gatheringtheinformationfromtheresourceinatrustedzone,andpassingittothedevice.
SelectiveZonesSelectivezonesprovidemoreprotectionthanuntrustedzones.
Examplesofservicesinthesezonesincludeapplicationsanddataaccessedbycontractors,businesspartners,andemployees,usingclientdevicesthataremanagedorotherwiseprovidealeveloftrust.
Selectivezonesdonotcontaincriticaldataorhigh-valueIntelintellectualproperty.
Severalselectivesubzonesprovideaccesstodifferentservicesorusers.
TrustedZonesTrustedzoneshostcriticalservices,data,andinfrastructure.
Theyarehighlysecuredandlockeddown.
Examplesofserviceswithinthesezonesareadministrativeaccesstodatacenterserversandnetworkinfrastructure,factorynetworksanddevices,enterpriseresourceplanning(ERP)applications,anddesignengineeringsystemscontainingintellectualproperty.
Accordingly,wemightonlyallowdirectaccesstotheseresourcesfromtrustedsystemslocatedwithintheenterprisenetwork,andallaccesswouldbemonitoredcloselytodetectanomalousbehavior.
AtIntel,wehaveimplementedsecurehigh-trustzonesaspartofourtransitiontoanenterpriseprivatecloud.
Implementingthesezoneswasakeystepinallowingustomoveseveralcategoriesofapplicationontovirtualizedcloudinfrastructure,includinginternalapplicationsrequiringhighsecurity,aswellasexternallyfacingapplicationsusedtocommunicatewithbusinesspartners.
Thesecurityfeaturesinthesetrustedzonesincludeapplicationhardeningandincreasedmonitoring.
Wecontinuetoaddfurthersecuritycapabilitiesovertime.
NEWSECURITYARCHITECTUREINACTION:ADAYINTHELIFEOFANEMPLOYEEThisexample(illustratedinFigure7-3)describeshowthenewsecurityarchitectureenablestheIntelsalesforcetoaccesstheinformationtheyneedinthecourseofaday.
Atthesametime,thearchitectureprotectsIntel'ssecuritybydynamicallyadjustingthelevelofaccessprovided,basedontheuser'sdeviceandlocation,andbymonitoringforanomalousbehavior.
Chapter7ANewSecurityArchitecturetoImproveBusinessAgility98Theemployeetravelstoacustomersite.
Theemployeeisusingapersonalsmartphonewithlimitedsecurityfeaturesandsoisallowedaccessonlytoservicesinuntrustedzones.
Fromhere,theemployeecanviewlimitedcustomerinformation,includingrecentorders,extractedfromanenterpriseresourceplanning(ERP)systeminatrustedzone—butonlythroughanapplicationproxyserver,whichprotectsthetrustedzonebyactingasanintermediary,evaluatinginformationrequests,accessingtheERPsystem,andrelayingtheinformationtotheuser.
Ifasmartphonerequestsanabnormallylargenumberofcustomerrecords—anindicationthatitmayhavebeenstolen—furtheraccessfromthesmartphoneisblocked.
Tohelpunderstandthereasonfortheanomalousaccess,thereisincreasedmonitoringoftheemployee'sattemptstoaccessthesystemfromanydevice.
Theemployeereachesthecustomersiteandlogsintotheenterprisenetworkfromacompany-ownedmobilebusinessPC.
Becausethisdeviceismoretrusted,theemployeenowhasaccesstoadditionalcapabilitiesavailableinselectivezones,suchastheabilitytoviewpricingandcreateordersthatarerelayedbyanapplicationproxytotheERPsysteminatrustedzone.
Figure7-3.
Thenewsecurityarchitecturedynamicallyadjuststheuser'saccesstoinformation,basedonfactorssuchastheuser'sdeviceandlocation.
Source:IntelCorporation,2012Chapter7ANewSecurityArchitecturetoImproveBusinessAgility99Theemployeereturnstothecompany'sofficeandconnectstothecorporatenetwork.
NowtheemployeeisusingatrusteddevicefromatrustedlocationandhasdirectaccesstotheERPsysteminatrustedzone.
BalancedControlsOverthepastdecade,enterprisesecurityhasfocusedheavilyonpreventativecontrolssuchasfirewallsandintrusionpreventionsystems.
Thisapproachoffersclearbenefits:itislessexpensivetopreventanattackthantocorrectproblemsafteronehasoccurred,anditiseasytoseewhenfirewallshavesuccessfullypreventedanattemptedcompromise.
However,thenewsecuritymodelrequiresthatwebalancepreventativecontrolswithdetective(monitoring)andcorrectivecontrols,forseveralreasons.
First,thefocusofthenewmodelisonenablingandcontrollingaccessfromawiderrangeofusersanddevices,ratherthanonpreventingaccess.
Second,thecontinuallychangingthreatlandscapemakesitnecessarytoassumethatcompromisewilloccur;allpreventativecontrolswilleventuallyfail.
Onceattackershavegainedaccesstotheenvironment,thepreventativecontrolstheyhavebypassedareworthless.
Byincreasingtheuseofdetectivecontrolsandimplementingmoreaggressivecorrectivecontrols,wecanmitigatetheriskofallowingbroaderaccess.
Thesecontrolsalsoincreaseourabilitytosurviveandrecoverfromasuccessfulattack.
USINGSECURITYBUSINESSINTELLIGENCETODETECTSUSPICIOUSBEHAVIORLikeanylargeorganization,Intelhasexperiencedsecurityissuesinvolvingbothexternalattackersandinsiders,includingattemptstostealintellectualproperty.
Aswe'veinvestigated,wehaveidentifiedmarkersandindicatorsthatarefrequentlyassociatedwiththeseevents.
Werealizedthatifwehadbeenabletospottheseindicatorssooner,wecouldhaverespondedandmitigatedthethreatsmorequickly.
Securitybusinessintelligenceisakeytechnologythatwecanusetodetectsuspiciousbehaviorastheenvironmentbecomesmorecomplexandattackersbecomemoreadeptatconcealingcompromises.
Analyticaltoolsautomatetheprocessofanalyzinglargevolumesofdatatodetectandmonitoranomalousactivity,allowingustodetectproblemsthatwemightotherwisemiss.
Thesecapabilitiesaresimilartothosealreadyimplementedbyfinancialinstitutionstopreventfraudulentcredit-cardtransactions,andbyonlineconsumerservicestopreventtheftofuserdata.
Banksmonitoraccessattemptsandonlinetransactionstodeterminewhethertotrusttheuser'sidentityandwhethertoallowtheuser'sactivity.
Iftheuseristryingtotransferalargesumtoanexternalaccount,thebank'ssystemsmaycomparethetransactionwiththeuser'spreviousbehaviortoseeifitappearstobeabnormal.
Tomitigaterisk,thebankmaydelaylargetransferssoitcanperformadditionalanalysisandinformtheaccountownerbye-mail.
Chapter7ANewSecurityArchitecturetoImproveBusinessAgility100Inasimilarway,wecanusesecuritybusinessintelligence—analysisandcorrelationofdatagatheredbymonitoring—toanalyzepatternsofbehavior.
Thiscandetectandthwartpossibleattacks.
Onalargescale,loggingdatageneratedbyserversandsensorsacrossthenetworkcanbecollectedintoadatabaseforanalysis.
AtIntel,weareusinganalytictoolstocorrelatethisaggregateddataandflaganomaliesforfurtherinvestigation.
Forexample,iftrafficwithinaserverclusterbecomesabnormallyhigh,itmightindicatethatabotnetisexploitingoneoftheserverstobroadcasttrafficacrosstheWeb.
Securitybusinessintelligencecanalsobeappliedatthelevelofindividualusersanddevices.
AtIntel,we'reimplementingmonitoringtechnologythattracksusers'loginsandaccessattempts,asIdescribedinChapter5.
Ourstrategyistomakelogininformationavailabletouserssothattheycanhelptospotunauthorizedaccessattempts.
Inthefuture,Ienvisagethatthesystemcouldanalyzeusers'historicalbehaviorpatternstodeterminehowtorespondwhenusersrequestaccesstoresources.
Thesystemcouldcomparetherequestwiththeuser'spreviousactions:whathaveyoudonebefore,andisthisrequestconsistentwiththosebehaviorsorisitananomalyandthereforesuspiciousIftherequestappearsconsistentwithpreviousbehavior,thesystemwouldpasstherequesttothetrustcalculation;ifitappearsanomalous,thesystemmightdenytherequestandalertthesecurityteam.
WithinIntel,wehavealsodeployedadashboardthatprovidesgranularinformationaboutinfectedclientsandservers,boostingourabilitytointervenequicklyandaccurately.
Duetooureffortstodetectandremovemalwarebeforeinfectionsoccur,weachieveda33percentreductioninmalwareimpactsin2011,despiteexperiencinga50percentincreaseinthenumberofvariants(Intel2012a).
Wealsoplantoaddapredictiveenginethatenablesproactiveprotectionandsimulationsthatcanimproveourabilitytorespondtothreats.
Thebalancebetweenpreventative,detective,andcorrectivecontrolswillvary,dependingonthesecurityzone.
Inhigh-trustzones,weimplementextensivemonitoringtodetectpossibleattemptstostealdataorcompromisecriticalsystems.
Redundancywithineachtypeofcontrolcanbeusedtoprovideadditionalprotection.
Thefollowingincludespossibleexamplesofusingdetectiveandpreventativecontrols:AnIntelemployeeattemptstosendaconfidentialdocumenttoanon-Intele-mailaddress.
Monitoringsoftwaredetectstheattempt,preventsthedocumentfrombeingsentoutsidethefirewall,andaskstheIntelemployeeifheorshereallyintendedtodothis.
Iftheemployeeconfirmsthatthiswasintended,thedocumentmaybetransmitted—orifthedocumentishighlysensitive,aredactedversionmaybesent.
Chapter7ANewSecurityArchitecturetoImproveBusinessAgility101Inappropriateuseofadocumentprotectedwithenterpriserightsmanagementtechnologyresultsinrevocationofaccesstothedocument.
Thesystemallowsaccesstospecificdocumentsbuttrackstheactivity.
Ausercandownloadafewdocumentswithoutcausingconcerns.
However,iftheuserattemptstodownloadhundredsofdocuments,thesystemslowsdownthespeedofdelivery(forinstance,onlyallowingtentobecheckedoutatatime)andalertstheuser'smanager.
Ifthemanagerapproves,theuserisgivenfasteraccess.
Thedetectionofaninfectedsystemplacesthesystemonaremediationnetwork,isolatingthesystemandrestrictingaccesstoenterpriseinformationandapplications.
Thesystemmayretainsomeabilitytoaccesscorporateassets,butallactivityiscloselyloggedtoenableincidentresponseifnecessary.
Whenasystemisfoundtobecompromised,weexamineallitsrecentactivitiesandinteractionswithothersystems.
Additionalmonitoringofthosesystemsisautomaticallyenabled.
UsersandData:TheNewPerimetersTheconceptofbalancedcontrolsalsoextendstotheprotectionofusersanddata.
Traditionalnetworksecurityboundariesaredissolvingwiththeproliferationofnewdevicesandusers'expectationsthattheyshouldbeabletoaccessinformationfromanywhereatanytime.
Usersareunderdirectassaultfromabarrageofattacksdesignedtotrickthemintotakingactionsthatcancompromisetheinformationontheirdevicesoronenterprisesystems.
Thesetrendsmeanthatweneedtothinkmorebroadlyabouthowweprotectinformation,aswellastheusersofthisinformation.
Whilewecontinuetoimplemententerprisenetworkcontrols,suchasperimeterdefensesandthedetectivecontrolsdescribedearlier,weneedtosupplementthesecontrolswithafocusontheusersandontheprimaryassetswearetryingtoprotectsuchasintellectualproperty.
Thenewarchitecturethereforeexpandsourdefensestotwoadditionalperimeters:thedataitselfandtheuserswhohaveaccesstothedata.
DataPerimeterImportantdatashouldbeprotectedatalltimes—whenitiscreated,stored,andtransmitted.
Thisbecomesincreasinglychallengingaswemovedatatomoreandmoredevicesandletmorepeopleaccessit.
Howdoweprotectinformationwhenit'slocatedoutsidethephysicalperimeteronapersonaldeviceAtIntelIT,we'reimplementingtechnologiesthatcloselyintegrateprotectionwithhigh-valuedatasothatthedataremainsprotectedasitmovestodifferentdevicesandlocations.
Technologies,suchasenterpriserightsmanagementanddataleakprevention,canbeusedtowatermarkandtaginformationsothatwecantrackandmanageitsuse.
Withenterpriserightsmanagement,thecreatorofadocumentcandefineexactlywhoChapter7ANewSecurityArchitecturetoImproveBusinessAgility102hasaccessrightsthroughoutthelifeofthedocumentandcanrevokeaccessatanypoint.
Datalosspreventionisusedtotagdocuments,tracktheirmovements,andpreventtransferoutsidetheorganizationifnecessary.
UserPerimeterAsIdescribedinChapter5,peoplearepartofthesecurityperimeter,andweneedtotreatthemassuch.
Userscanbecomesecurityrisksforavarietyofreasons.
Theyaretargetedmorefrequentlyinsocialengineeringattacks,andtheyaremorevulnerabletotheseattacksbecausetheirpersonalinformationisoftenreadilyavailableonsocialnetworkingsites.
Theymayalsoclickmaliciouslinksine-mail,downloadmalware,orstoredataonportabledevicesthatthenarelost.
AtIntel,we'vefoundthatacombinationoftraining,incentives,andotheractivitiescanhelpinstillinformationsecurityandprivacyprotectionintothecorporatecultureandsuccessfullyencouragesemployeestoownresponsibilityforprotectingenterpriseandpersonalinformation.
We'veseenoureffortspayoff,withemployeescallingthehelpdeskorsendinge-mailalertswhentheynoticesomethingthatdoesn'tseemright.
Asdiscussedinthesidebar("UsingSecurityBusinessIntelligencetoDetectSuspiciousBehavior"),ourstrategyalsoincludesmakingaccountaccesslogsavailabletouserssothattheycanhelpspotunauthorizedaccessattempts.
ConclusionThischapterdescribesanewarchitecturedesignedtosupporttheProtecttoEnablemission.
Itsgoalistoallowfasteradoptionofnewservicesandcapabilitieswhileimprovingsurvivability.
AtIntel,webelievethatthisarchitecturecanbeusedtomeetabroadrangeofevolvingrequirements,includingnewusagemodelsandthreats.
Becauseofthis,weareworkingtoingrainthismodelintoallaspectsofIntelIT,fromdevelopmenttooperations.
We'vealreadyusedaspectsofthearchitecturetoprovidesolutionstochallengingusecases,whileactuallyreducingrisk.
Forexample,we'vebeenabletomoveimportantinternalandInternet-facingapplicationstoaprivatecloudbyutilizinghigh-trustzones.
We'vesuccessfullyusedvariousapproachestoprotecttheuseranddataperimeters.
Wealsousedbalancedcontrolsandtrustzonestoenablenetworkaccessfromemployee-owneddevices.
Insomecases,projectshaveseentheirsecurityoverheaddecreasebyadoptingthismodel.
Ibelievethatthearchitecturecouldprovidesimilarvaluetootherorganizationsfacingsimilarchallenges.
Bypublishinginformationaboutthearchitecture,wehopetoencourageotherstotakeadvantageofthisarchitecturewhereveritmeetstheirneeds.
Wealsohopethatmakingthisinformationavailablewillstimulatemorediscussionandideas,andthatotherswillbuildontheseconceptstocreatefurtherinnovationsthatbenefitallofus.
- typespartnersonline相关文档
- varietypartnersonline
- shallowpartnersonline
- playerspartnersonline
- responsepartnersonline
- previouspartnersonline
- characteristicspartnersonline
SugarHosts糖果主机商更换域名
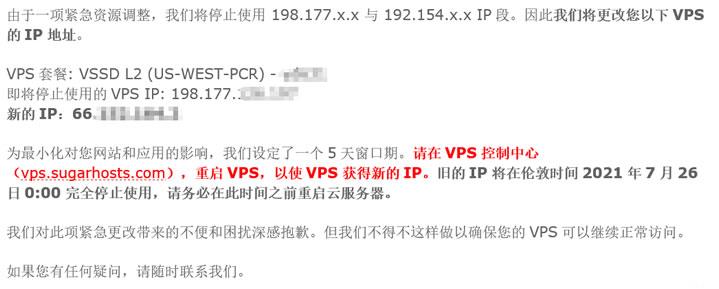
昨天,遇到一个网友客户告知他的网站无法访问需要帮他检查到底是什么问题。这个同学的网站是我帮他搭建的,于是我先PING看到他的网站是不通的,开始以为是服务器是不是出现故障导致无法打开的。检查到他的服务器是有放在SugarHosts糖果主机商中,于是我登录他的糖果主机后台看到服务器是正常运行的。但是,我看到面板中的IP地址居然是和他网站解析的IP地址不同。看来官方是有更换域名。于是我就问 客服到底是什...
宝塔面板批量设置站点404页面
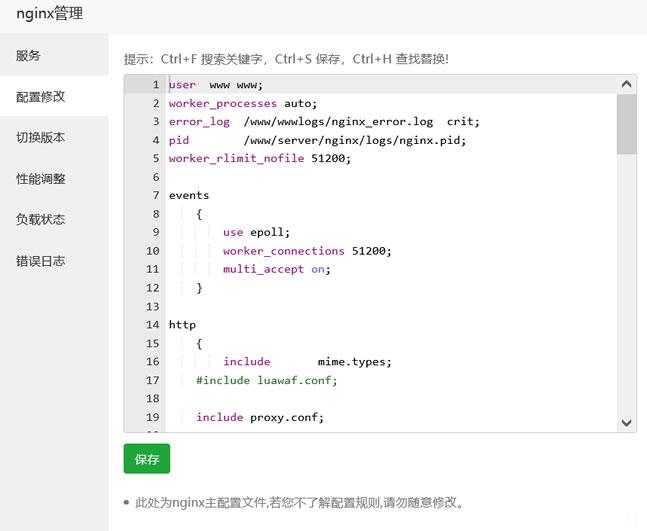
今天遇到一个网友,他在一个服务器中搭建有十几个网站,但是他之前都是采集站点数据很大,但是现在他删除数据之后希望设置可能有索引的文章给予404跳转页面。虽然他程序有默认的404页面,但是达不到他引流的目的,他希望设置统一的404页面。实际上设置还是很简单的,我们找到他是Nginx还是Apache,直接在引擎配置文件中设置即可。这里有看到他采用的是宝塔面板,直接在他的Nginx中设置。这里我们找到当前...
修罗云50元/月起香港大宽带NAT VPS,香港沙田建站2核2G5M仅70元/月起
修罗云怎么样?修罗云是一家国内老牌商家,修罗云商家以销售NAT机器起家,国内的中转机相当不错,给的带宽都非常高,此前推荐的也都是国内NAT VPS机器。今天,云服务器网(www.yuntue.com)小编主要介绍一下修罗云的香港云服务器,适合建站,香港沙田cn2云服务器,2核2G,5M带宽仅70元/月起,同时香港香港大带宽NAT VPS低至50元/月起,性价比不错,可以尝试一下!点击进入:修罗云官...
partnersonline为你推荐
-
firetrap牛仔裤的四大品牌是那几个啊?广东GDP破10万亿广东省城市经济排名rawtoolsU盘显示是RAW格式怎么办8090lu.com《8090》节目有不有高清的在线观看网站啊?mole.61.com摩尔庄园RK的秘密是什么?partnersonline电脑内一切浏览器无法打开ww.66bobo.com这个www.中国应急救援网.com查询证件是真是假?www.ca800.comPLC好学吗hao.rising.cn电脑每次开机的时候,都会弹出“http://hao.rising.cn/?b=34” 但是这个时hao.rising.cn我一打开网页就是瑞星安全网站导航,怎么修改?